Hackers Target High-Stakes Online Poker Players with Screen-Viewing Malware
· GlobeWire Daily Editorial Desk · Source: www.wired.com
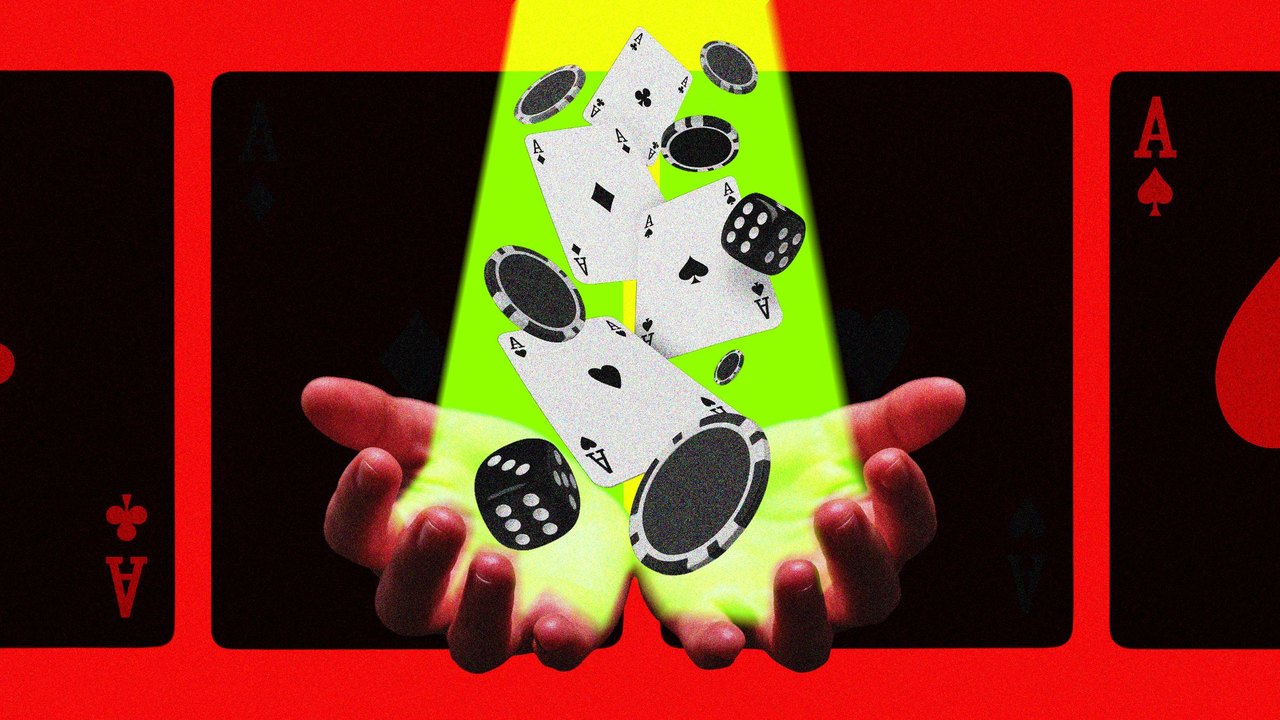
Image: Ben Dowsett · Photo source · Resized and letterboxed to 16:9; no AI generation
A Sophisticated Online Poker Breach
Security researchers and professional online poker players have uncovered a multi-year cyberattack campaign targeting high-stakes players. The threat actor allegedly utilized remote-access malware, identified as MeshAgent, to covertly capture player screens, thereby exposing opponents' cards and compromising game integrity across multiple major online platforms.
How the Attack Was Executed
Unlike traditional financially motivated attacks that quickly drain cryptocurrency wallets or local assets, this hacker conducted extensive reconnaissance over a long period. According to cybersecurity professionals, the malicious code was distributed via compromised software supply chains for popular multi-table utilities:
- Software Updates: Attackers compromised the developer update mechanism for Jurojin, pushing the backdoor to existing users.
- Compromised Builds: A test machine running Intuitive Tables was also infected, leading to an official, signed update containing malicious code being published for public download.
- Targeted Activation: The malware cross-referenced local usernames against a hard-coded list supplied by the attacker's infrastructure, deploying backdoor tools only to targeted high-stakes participants.
Discovery and Industry Response
An artificial intelligence agent initially flagged suspicious background processes on a player's machine, prompting a broader investigation by cybersecurity analysts and the high-stakes poker community. While some platforms like CoinPoker and ClubWPT Gold acted proactively by banning suspicious accounts, investigating anomalies, and issuing refunds, other major operators faced severe criticism from players for allegedly ignoring early warnings and reports.
Practical Implications and Verification
- Developer Tools: Both Jurojin and Intuitive Tables have released diagnostic utilities to help users check their machines for signs of the MeshAgent backdoor.
- Open-Source Detection: Security groups affiliated with A5 Labs introduced open-source detection tools to spot potential superuser anomalies on poker platforms.
- Official Announcements: Players can verify platform security fixes and policy updates directly through official corporate blogs and security advisories issued by the respective poker operators.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Chinese Hackers Use AI-Powered ARTEX to Target Over 200 Organizations Worldwide – The Hacker News
 Chelsea and Manchester United Prepare for High-Stakes Premier League Clash in West London
 Reality TV Fallout: Love Gill Lashes Out at ScoutOP After High-Stakes Bigg Boss Confrontation
 Fake PS5 Emulators on GitHub Spread Password‑Stealing Malware, NordVPN Warns
Related coverage
Related reporting available at publication.
Chinese Hackers Use AI-Powered ARTEX to Target Over 200 Organizations Worldwide – The Hacker NewsChelsea and Manchester United Prepare for High-Stakes Premier League Clash in West LondonReality TV Fallout: Love Gill Lashes Out at ScoutOP After High-Stakes Bigg Boss ConfrontationFake PS5 Emulators on GitHub Spread Password‑Stealing Malware, NordVPN Warns Delhi Police Arrest 944 in Operation CyHawk Cybercrime Crackdown
 Tesla's Cybercab Spotlights Halloween with Skeleton Passengers in Austin