Recent Cybersecurity Trends: From Supply Chain Vulnerabilities to AI-Driven Phishing
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Escalating Threats in the Digital Landscape
Recent reports from The Hacker News highlight a surge in complex cyber threats targeting both infrastructure and individual data security. Security professionals and organizations are urged to monitor several emerging vectors that currently pose significant risks:
- Hardware and Firmware Vulnerabilities: Manufacturers are increasingly forced to address fundamental trust issues. A notable example includes Keystone's decision to decommission thousands of hardware wallets following a security breach involving device verification keys, underscoring the dangers of supply chain compromises.
- Software Supply Chain Attacks: Malicious actors continue to exploit administrative software, with groups like Lazarus leveraging regional security software in South Korea to facilitate malware deployment via post-quantum encryption techniques.
- Web and Application Security: The prevalence of Remote Code Execution (RCE) flaws remains a critical issue. Recently, CISA identified active exploitation of PHP-based vulnerabilities, while researchers discovered critical flaws in Wasmtime that could allow WebAssembly modules to bypass critical sandbox protections.
- AI and Social Engineering: The integration of AI in cybercrime has reached new levels of sophistication. From AI-generated fake login portals that bypass traditional security filters to Microsoft Teams IT support scams, attackers are increasingly using automated tools to gain unauthorized access.
- IoT and E-commerce Risks: Vulnerabilities in Dahua IP cameras and the injection of scanner-evading JavaScript into Magento-based online stores demonstrate that edge devices and retail platforms remain high-value targets for data exfiltration.
Practical Steps for Mitigation
Organizations should consider the following measures to improve their security posture:
- Implement Rigorous Audits: Regularly scan for "Shadow AI" usage within company networks to ensure unauthorized or unsecured AI tools do not become entry points for attackers.
- Verify Software Updates: Given the frequency of patches for core technologies like PHP, ensure that all server-side environments are updated immediately upon release to mitigate RCE risks.
- Token Security: Following reports of token-replay attacks on Microsoft 365 and the misuse of GitHub Actions logs, implement strict session management policies and rotate secrets frequently.
For verification of specific vulnerabilities, professionals should consult the official CVE databases and CISA's Known Exploited Vulnerabilities (KEV) catalog.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Supermarket Freezers in Belgium and Sweden Hit by Suspected Cyber-Attack
 Surfpunk Emerges as a Unique Indie RPG Contender Following Steam Next Fest
 Navigating Holiday Scams: Essential Cyber Safety Guidelines for Online Shoppers
 Reddit Plans to Restrict Unauthenticated Access to Combat Scraping and Boost Personalization
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 BMW G310R: Motorcycle Specifications, Facts and Verification Guide
 Yamaha FZR400: Motorcycle Specifications, Facts and Verification Guide
 Maxus EV30: Car Specifications, Facts and Verification Guide
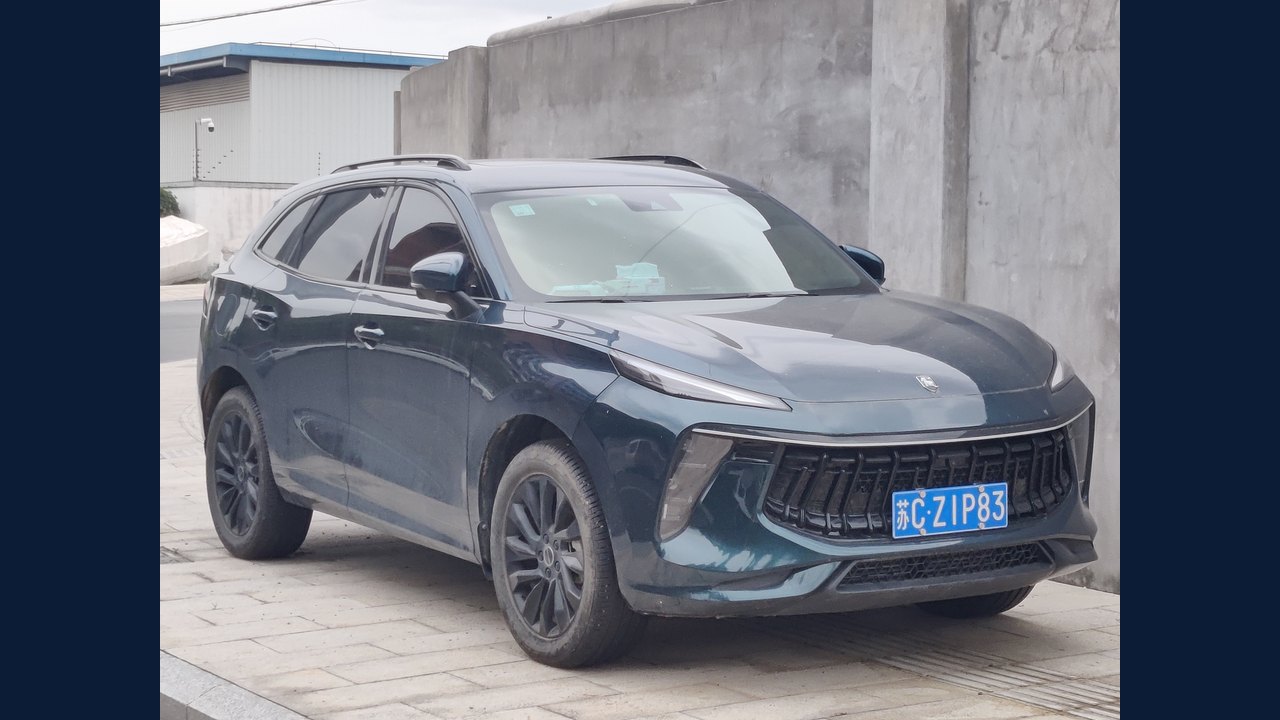 Forthing T5 EVO: Car Specifications, Facts and Verification Guide
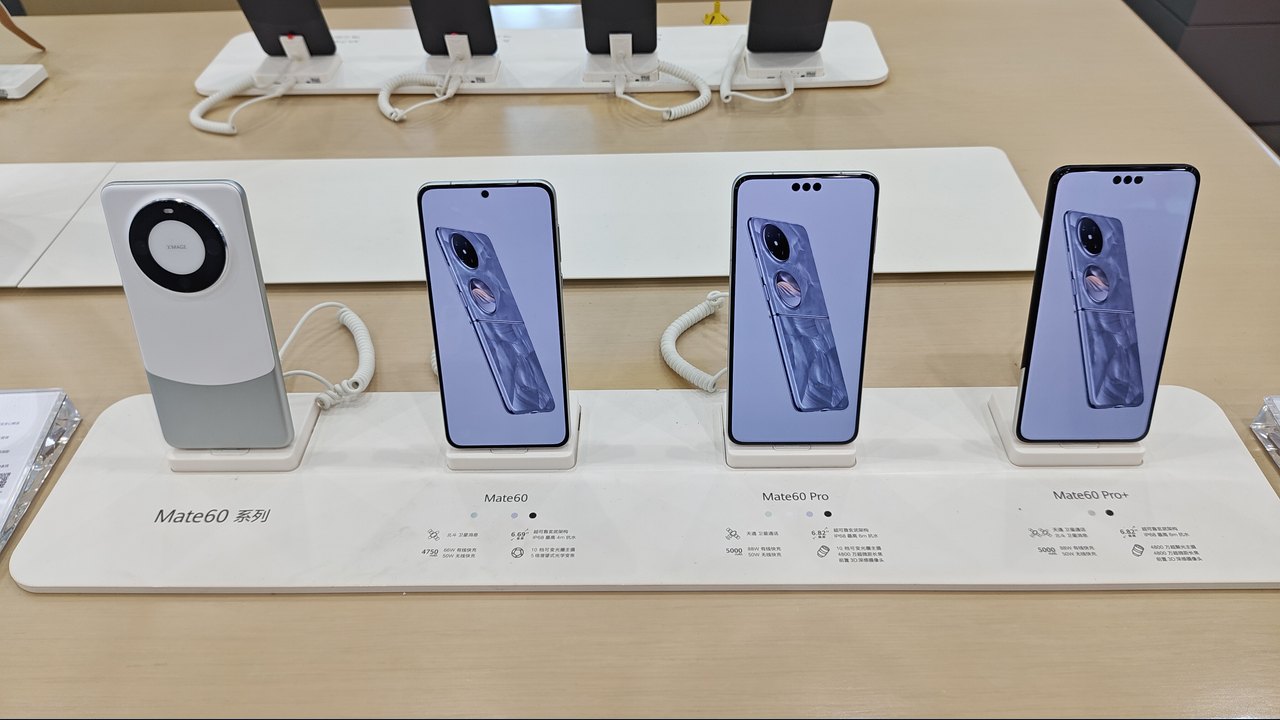 Huawei Mate 60: Smartphone Specifications, Facts and Verification Guide
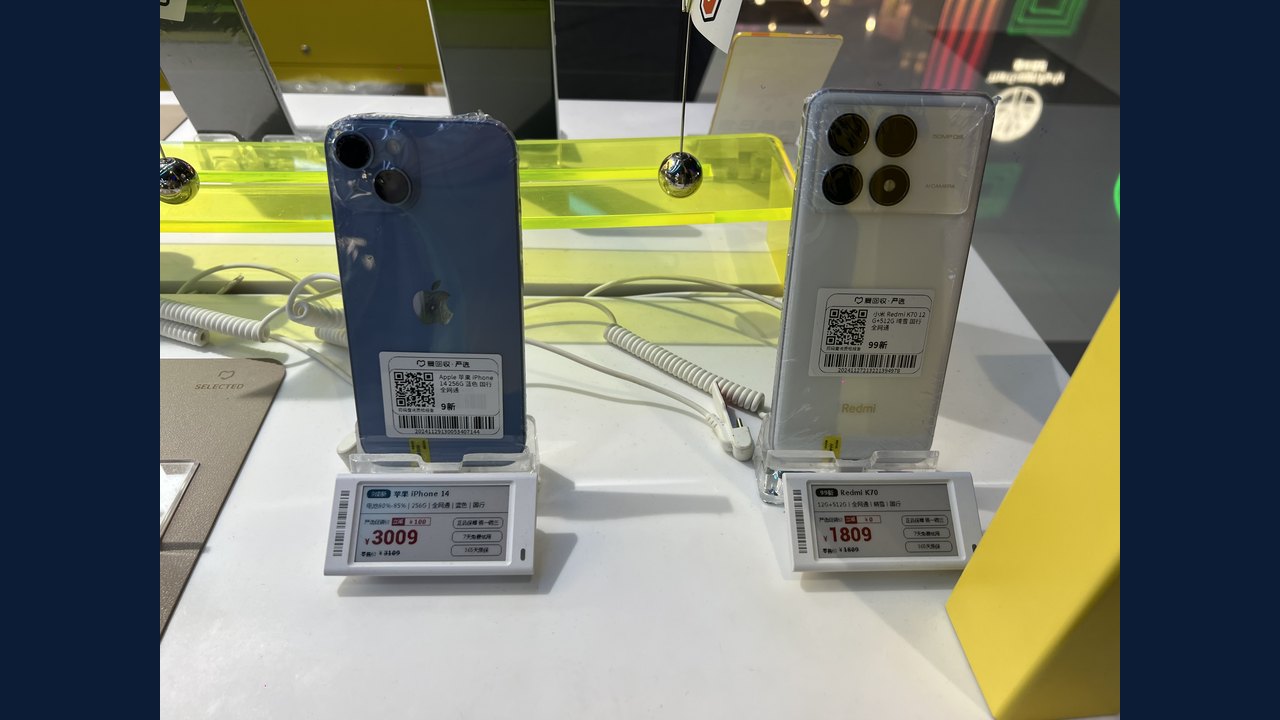 Redmi K70: Smartphone Specifications, Facts and Verification Guide