GitHub Announces Public Preview of AI Scan for Entire Repositories
· GlobeWire Daily Editorial Desk · Source: github.blog
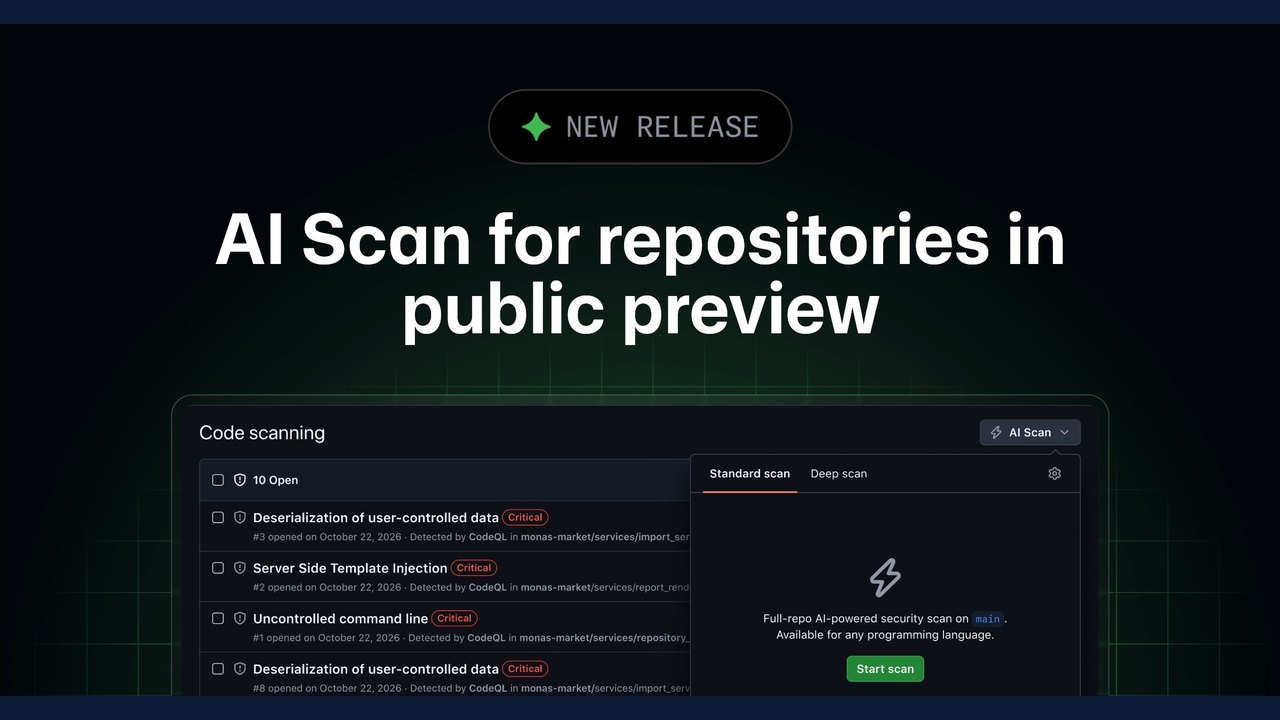
Image: The GitHub Blog · Photo source · Resized and letterboxed to 16:9; no AI generation
Overview of AI Scan
GitHub has announced the public preview of AI Scan for repositories, expanding vulnerability detection across an entire codebase rather than limiting analysis to pull request changes. According to the announcement, the feature utilizes an agentic code scanner designed to explore repositories and target code sections most likely to contain security vulnerabilities.
The system is intended to complement existing tools like CodeQL. It supports languages and frameworks not currently covered by CodeQL and aims to identify issues that rule-based analysis might miss in supported languages.
Key Features and Integration
- Unified Alerts: Findings from AI Scan appear directly in the standard GitHub code scanning alert list alongside CodeQL alerts.
- Duplicate Prevention: When both AI Scan and CodeQL operate on the same repository, AI Scan is designed to skip issues already reported by CodeQL.
- Workflow Compatibility: Alerts integrate into existing code scanning workflows, supporting assignees, linked pull requests, and security campaigns.
- Autofix Support: Developers can address findings using agentic autofix capabilities.
Activation and Availability
Access to AI Scan depends on account type and tier:
- Enterprise and Organizations: Available on github.com and GitHub Enterprise Cloud with data residency for public, private, and internal repositories, provided the organization utilizes GitHub Code Security or GitHub Advanced Security. Enterprise administrators must enable the policy first.
- Personal Accounts: Available for public repositories only; private personal repositories are not supported.
Usage of the feature consumes Code Security AI credits, which are tracked in enterprise billing sections. A GitHub Copilot license is not required to use AI Scan.
Verification and Next Steps
Users with write access to code scanning can initiate scans from the Code scanning page once enabled. Unlike some automated checks, AI Scan alerts do not automatically close upon merging a fix; developers must run a new scan to verify and close resolved alerts.
To verify these details and read the official announcement, consult the GitHub Changelog or participate in discussions on the GitHub Community platform.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 GitHub Launches Public Preview of Code Scanning for AI and Agent Vulnerabilities
 Bihar Public Service Commission Announces TRE 4.0 Recruitment for 33,320 Teaching Positions
 GitHub Universe 2026 Announces Agentic Software Delivery System and Copilot Updates
 AI Firm Anthropic Files for Public Offering in Move Toward Historic Valuation
Related coverage
Related reporting available at publication.
GitHub Launches Public Preview of Code Scanning for AI and Agent VulnerabilitiesBihar Public Service Commission Announces TRE 4.0 Recruitment for 33,320 Teaching PositionsGitHub Universe 2026 Announces Agentic Software Delivery System and Copilot UpdatesAI Firm Anthropic Files for Public Offering in Move Toward Historic Valuation AI Startup Cathedral Claims It Used Autonomous Agents to Breach Anthropic Systems
 OpenAI Shifts Strategy to Train Frontier AI Models Without Live Internet Access