OpenAI Automated Pipeline Discovers 948 Linux Kernel Exploits in October 2026 Run
· GlobeWire Daily Editorial Desk · Source: www.artificialintelligence-news.com
Image: Ryan Daws · Photo source · Resized and letterboxed to 16:9; no AI generation
OpenAI reported that an automated kernel research pipeline identified 948 working local privilege escalation exploits during a single mid-October 2026 run. The disclosures were published under the Patch the Planet initiative, part of the Daybreak open-source security commitment. According to the report, the five-stage system operated on an upcoming cyber model and flagged thousands of candidate findings on the latest Linux kernel master branch.
Pipeline Workflow and Verification
The research effort incorporated multiple automated agents to filter, scan, and test the kernel codebase:
- Triage: Scout agents reviewed over 40 million lines of kernel code, narrowing the scope to 5,034 audit targets.
- Scanning: Analyst agents scanned the filtered set, producing a candidate list within half a day.
- Testing: Triage agents executed proof-of-concepts inside isolated virtual machines, confirming 1,724 real vulnerabilities.
- Exploitation: ExploitDev agents built working exploits, while human security researchers reviewed every exploit, patch, and severity rating before any upstream reporting.
Results and Testing Environments
The stock desktop distributions used in testing ran with hardware and software mitigations enabled, including SMEP, SMAP, KASLR, and HARDENED_USERCOPY. OpenAI noted that 74.7 percent of candidates survived dynamic validation, with model error accounting for just 3.1 percent of failures. Additionally, testing in Google’s kernelCTF environment produced 21 LPE exploits in a single campaign.
Costs and Upstream Remediation
The October campaign incurred $1,213,430 in API credits, averaging $1,279 per working root exploit. OpenAI noted this figure represents an upper bound that could potentially be reduced through harness engineering. Maintainers worked in parallel with the researchers; within 10 days of scanning and manual analysis, 61 of the discovered vulnerabilities had been patched upstream, with staging patches covering additional issues.
Practical Implications and Verification
OpenAI concluded that unpatched operating systems should be treated with heightened caution by administrators. Readers can review the original announcements and technical disclosures directly through OpenAI’s official security publications and GitHub repositories associated with the Patch the Planet initiative to verify these findings.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 OpenAI Rolls Out Automatic Creative Enhancements for ChatGPT Ads Starting October 30, 2026
 Critical Linux Kernel Flaw CVE-2026-98432 Allows Remote Root Attacks on MPTCP Servers
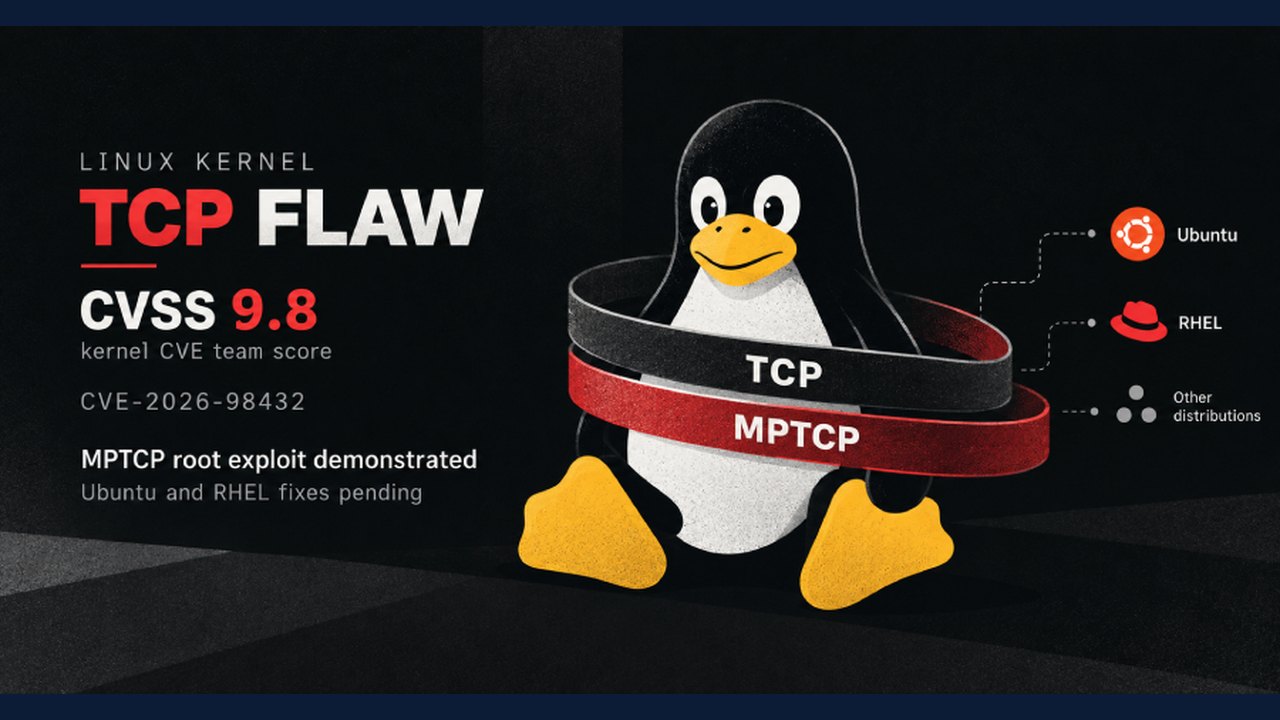 Linux Kernel TCP Vulnerability Tracked as CVE-2026-98432 Draws Attention
 Mitigating CVE-2026-98432: Linux Kernel IPv4 SYN Use-After-Free Vulnerability