Linux Kernel TCP Vulnerability Tracked as CVE-2026-98432 Draws Attention
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
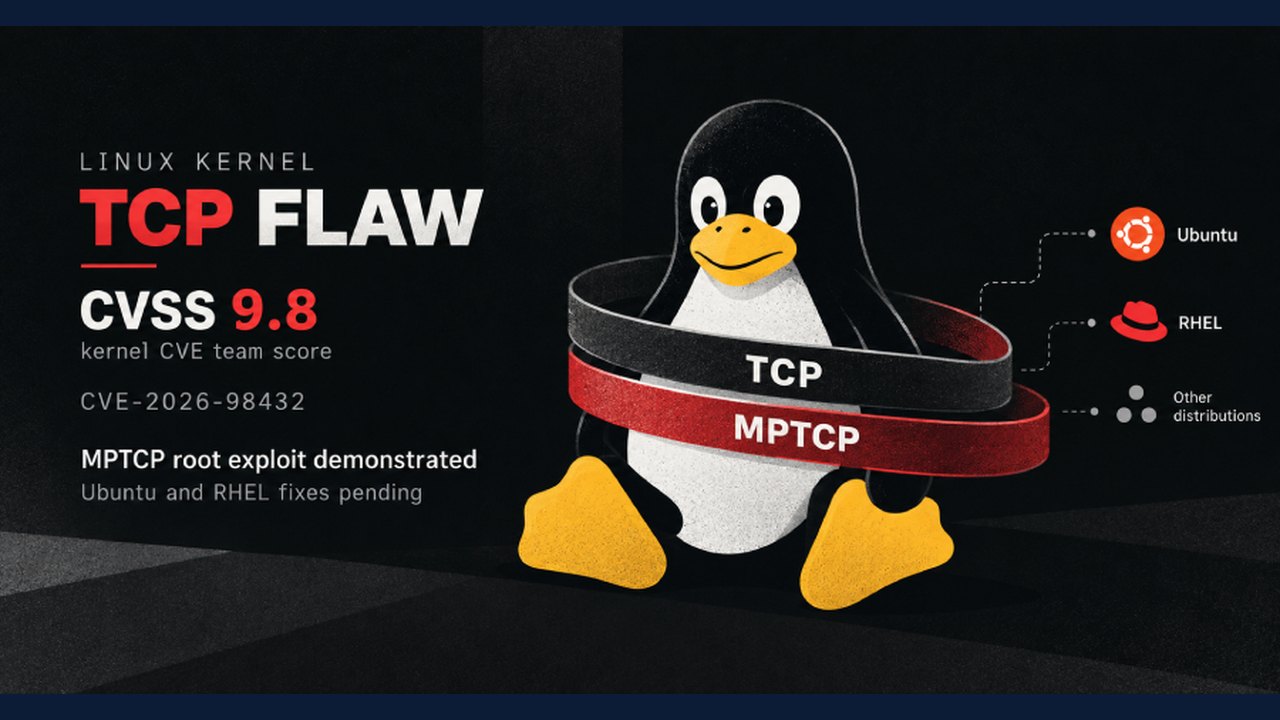
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
A recently discussed vulnerability in the Linux kernel's TCP code, tracked as CVE-2026-98432, has impacted multiple Linux distributions including Ubuntu and Red Hat Enterprise Linux (RHEL). The kernel's CVE team assigned a 9.8 out of 10 score on the CVSS scale, while various vendors have evaluated the severity differently ranging from 5.9 to 8.1.
Anthropic reported on October 27 that its AI model assisted in writing an exploit utilizing this flaw against servers featuring a multipath TCP listener. As of late October, while some distributions like Debian, Oracle Linux, SUSE, and Amazon Linux have shipped fixes, Ubuntu and RHEL have not yet released a fixed kernel package.
Understanding the Flaw and Impact
- Nature of the Bug: A use-after-free race condition during the IPv4 TCP handshake.
- Vendor Discrepancies: Red Hat, Amazon, Oracle, and SUSE assigned lower CVSS scores between 5.9 and 8.1 compared to the kernel team's 9.8.
- Exploitation Potential: Anthropic's demonstrated exploit involved bypassing KASLR and executing commands as root, though no active exploitation in the wild has been officially reported as of October 29.
Practical Implications and Verification
Administrators should review vendor security advisories to verify the deployment status of fixed kernels. If building kernels directly, upstream fixes are available in maintained stable branches. For Go-based applications, the Go Security Team noted that setting specific environment variables can disable MPTCP at runtime, though upgrading the underlying kernel remains the primary recommended solution.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Mitigating CVE-2026-98432: Linux Kernel IPv4 SYN Use-After-Free Vulnerability
 Critical Linux Kernel Flaw CVE-2026-98432 Allows Remote Root Attacks on MPTCP Servers
 Innora Security Research Publishes Linux Kernel Vulnerability and CVE Analysis Repository
 ESA Open Days 2026 Draws Over 23,000 Visitors Across Six Establishments
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 Madhya Pradesh Government Plans Revenue Generation from 117-Year-Old Edward Villa in Mumbai Through Leasing
 iPhone 18 Pro Named TechRadar Product of the Year 2026
 Google Project Suncatcher Runs Gemma 4 AI on Orbiting Satellite and Receives First Response
 Gender Disparities in Eye Care Access Across India Examined
 Satellite Images Show Cyclone Arnab Weakening Over India As New System Brews
 Expanding Green and Blue Spaces Crucial for India's Economic and Public Health, Reports Indicate