Technical Analysis of CVE-2026-111497: Pinned WordPress Image RCE Proof of Concept
· GlobeWire Daily Editorial Desk · Source: github.com
Image: GitHub · Photo source · Resized and letterboxed to 16:9; no AI generation
Overview of CVE-2026-111497
A proof-of-concept (PoC) repository has been published detailing a target-specific remote code execution (RCE) chain tracked as CVE-2026-111497. The research demonstrates unauthenticated command execution against a specific pinned Docker Official Image for WordPress. According to the published documentation, the mechanism relies on a combination of an XML-RPC pingback request and a manipulated Brotli decoding stream.
It is important to note that the findings apply exclusively to the tested image digest and make no claims regarding current WordPress images, other digests, or memory errors in WordPress Core.
How the Attack Vector Operates
The reported chain involves several distinct technical conditions:
- Inbound XML-RPC Request: A single unauthenticated `pingback.ping` request triggers WordPress to fetch an attacker-controlled URL twice during the same PHP request.
- Decoder Corruption: The first HTTP response corrupts a PHP handler through a malformed Brotli data stream. Specifically, it copies bytes from a live system handler pointer into the `strtolower` handler, leveraging the fact that both pointers share the same ASLR-loaded `libphp.so` base.
- Retry and Execution: After encountering a content encoding error, the HTTP transport retries without content decoding. The subsequent header reaches the modified handler, starting a fixed Bash command that reads a synthetic flag file, which is then returned in the XML-RPC response.
Prerequisites and Environment Requirements
The reported lab environment relies on strict constraints, including:
- Reachable `/xmlrpc.php` with `pingback.ping` enabled.
- A functioning post that accepts pingbacks and allows WordPress to fetch external URLs.
- Specific versions of Brotli, PHP, glibc, cURL, Requests, Apache, and the system memory allocator.
- Linux amd64 running rootless Podman with ASLR mode 2 enabled.
Verification and Mitigation Strategies
Security researchers and system administrators can review the repository scripts, such as `verify.sh` and `generate_payloads.py`, to inspect payload constants and serialization stages using the Python standard library.
To address potential exposure, administrators should apply the following steps:
- Update affected Brotli packages to vendor-fixed versions (such as upstream branches 1.0.10, 1.1.1, or 1.2.1, or appropriate distribution backports).
- Restart or redeploy all processes that loaded the vulnerable decoder libraries.
- Disable unused XML-RPC pingbacks and remove untrusted Brotli decoding paths until updates are fully applied.
Review official vendor advisories and changelogs to verify the exact status of installed packages.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 CVE‑2026‑112445: How a Mis‑configured macOS LaunchDaemon Lets Any User Gain Root
 Unpatched WordPress Sites Face Tens of Thousands of Attacks Following RCE Flaw Disclosure
 ARCI Recruitment 2026: Applications Open for 29 Technical, Administrative, and Scientific Posts
 New Claude Code Skill Turns Ambiguous AI Output into Simplified Technical English
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
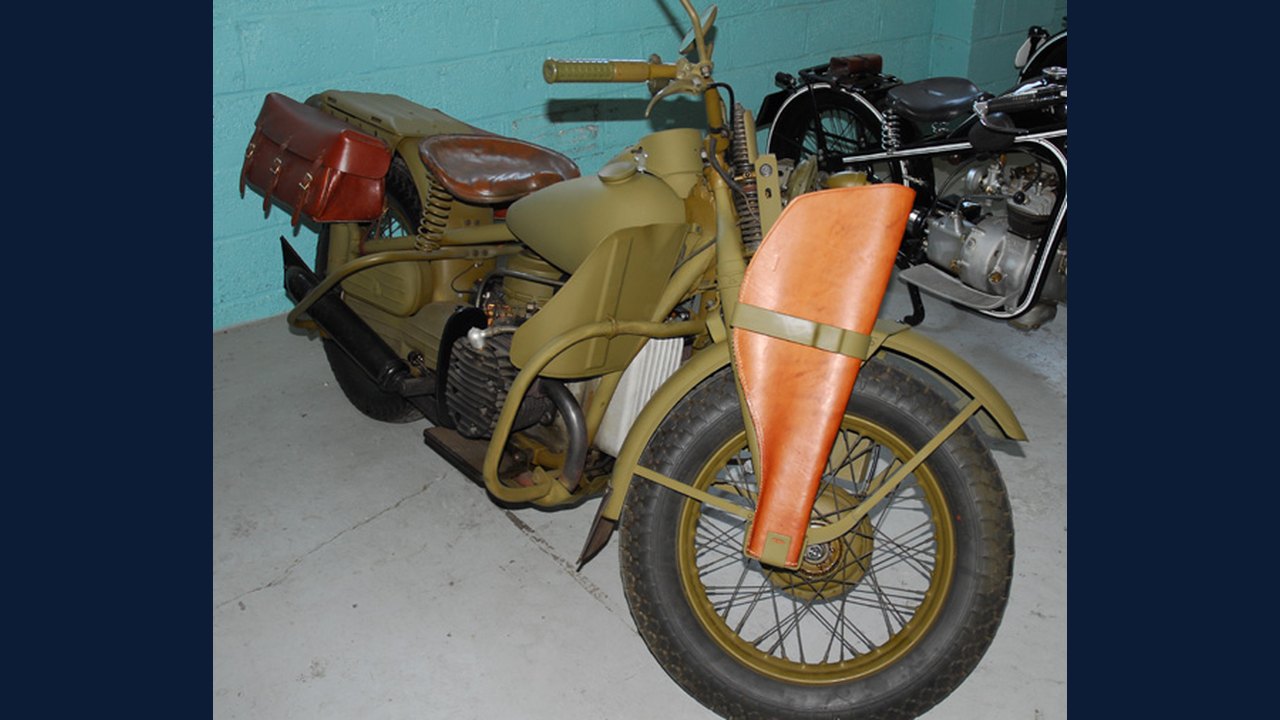 Harley-Davidson XA: Specifications & buying guide
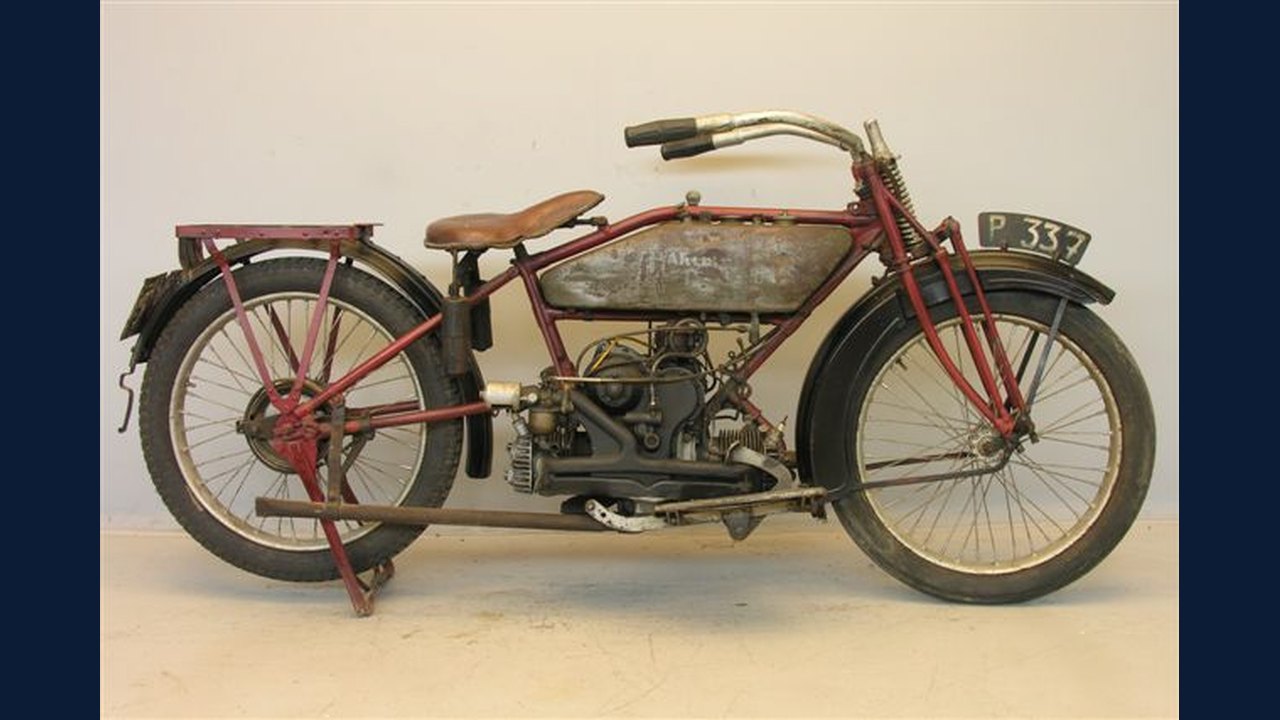 Harley-Davidson Model W: Specifications & buying guide
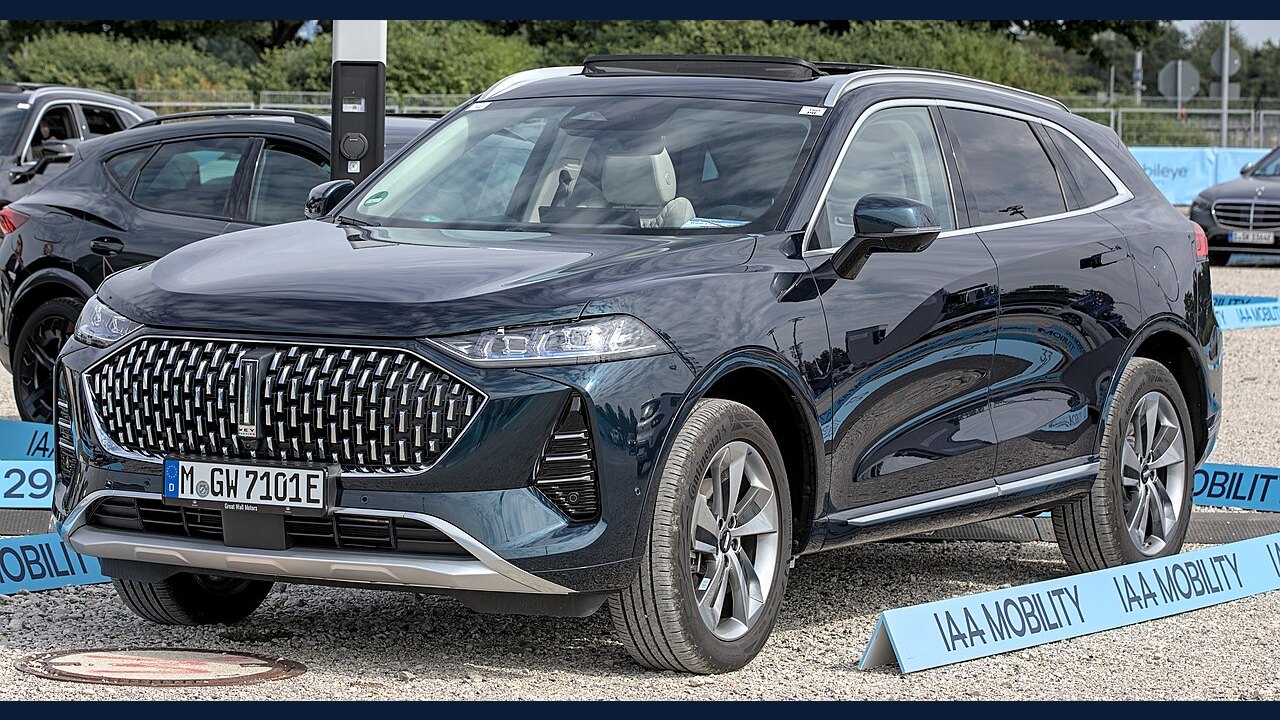 WEY Mocha: Specifications, variants & buying guide
 Ford Mondeo Sport: Specifications, variants & buying guide
 Nokia Lumia 1520: Specifications & buying guide
 Samsung Galaxy S4 Active: Specifications & buying guide