Cisco Addresses Actively Exploited VPN Vulnerability in ASA and FTD Firewalls
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
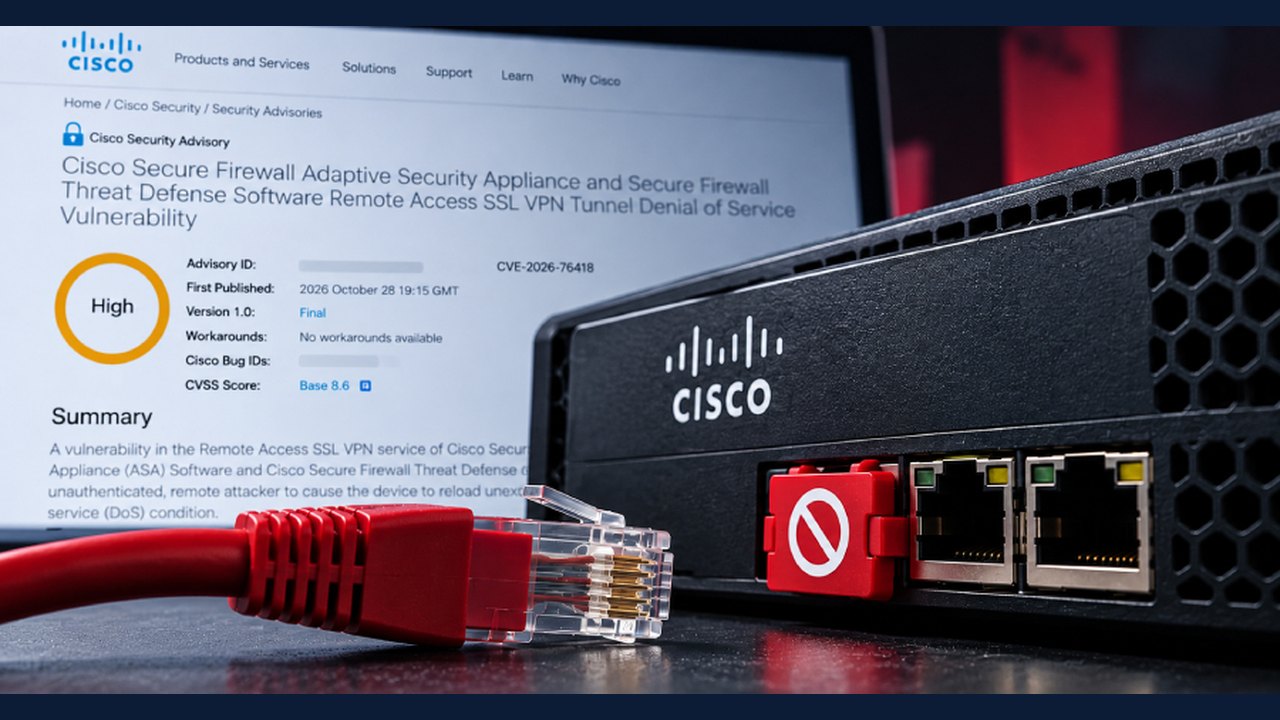
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Critical Vulnerability Identified
Cisco has issued security patches for a high-severity vulnerability, tracked as CVE-2026-76418, affecting its Secure Firewall Adaptive Security Appliance (ASA) and Secure Firewall Threat Defense (FTD) software. The flaw, which has a CVSS score of 8.6, is currently being exploited in the wild.
Impact and Technical Details
The vulnerability resides within the Remote Access SSL VPN service. It is triggered by a logic error when secondary authentication is configured on a tunnel group. An unauthenticated remote attacker can exploit this by sending a crafted request during an SSL VPN connection, forcing the affected device to reload and resulting in a denial-of-service (DoS) condition.
Vulnerable Configurations
Devices are at risk if:
- They run a vulnerable software version.
- The SSL remote access VPN service is enabled and reachable.
- Secondary authentication is configured in the tunnel group scope.
Remediation and Mitigation
Cisco has released updates for affected versions of ASA (e.g., 9.16.4.104, 9.24.10.1) and FTD (e.g., 7.7.14, 10.1.1). Administrators should verify their configurations:
- Check Tunnel Groups: Inspect all tunnel groups, including the default `DefaultWEBVPNGroup`, for the `secondary-authentication-server-group` setting.
- Temporary Mitigations: If patching is not immediately possible, consider disabling secondary authentication on relevant tunnel groups or disabling the tunnel group list if the default group does not utilize secondary authentication.
Users should consult the official Cisco Security Advisory to verify specific software versions and confirm implementation steps for their environment. This disclosure follows recent reports of separate advanced persistent threat activity targeting other Cisco infrastructure, underscoring the importance of timely patch management.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 CISA Adds Actively Exploited GitLab RCE and Cisco Firewall DoS Flaws to KEV Catalog
 Drupal Issues Urgent Patch for Critical Commerce Core Flaw Actively Exploited in Attacks
 St Mirren Boss McLeish Addresses Phillips Future and Injury Updates Ahead of Motherwell Clash
 Celtic Prepare for Falkirk Clash as Manager Martin O'Neill Addresses Squad and Tactics
Related coverage
Related reporting available at publication.
CISA Adds Actively Exploited GitLab RCE and Cisco Firewall DoS Flaws to KEV CatalogDrupal Issues Urgent Patch for Critical Commerce Core Flaw Actively Exploited in AttacksSt Mirren Boss McLeish Addresses Phillips Future and Injury Updates Ahead of Motherwell ClashCeltic Prepare for Falkirk Clash as Manager Martin O'Neill Addresses Squad and Tactics Binance Pledges to Cover Billions Following Record-Breaking Crypto Hack
 Binance Faces Major Security Breach Impacting Billions as Investigations Continue