Inside Modern Phishing Kits Built to Steal Microsoft 365 Sessions
· GlobeWire Daily Editorial Desk · Source: www.bleepingcomputer.com
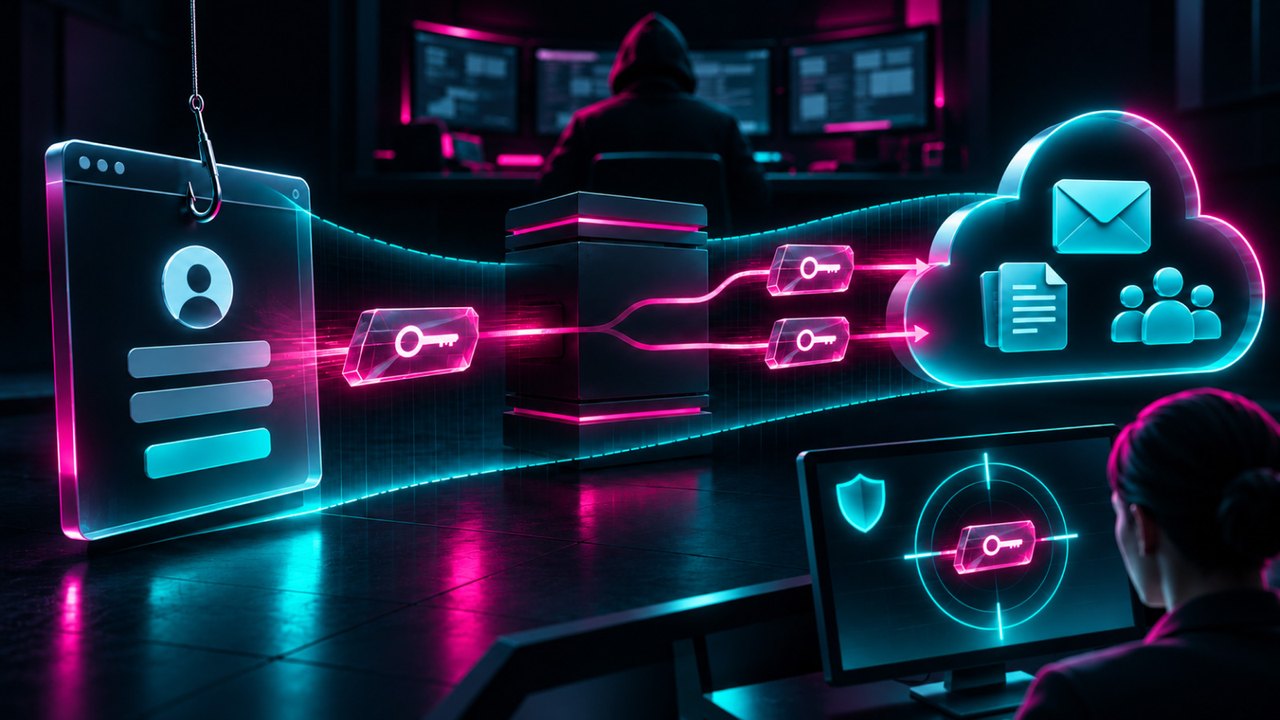
Image: BleepingComputer · Photo source · Resized and letterboxed to 16:9; no AI generation
Modern phishing kits have evolved into sophisticated software operations featuring admin dashboards and round-the-clock support, designed specifically to target and steal Microsoft 365 session tokens. According to security researchers at Huntress, these pre-packaged tools lower the barrier to entry for attackers, allowing them to bypass traditional login credentials and multi-factor authentication (MFA) to gain direct access to active cloud sessions and emails.
Understanding Token Theft and Tradecraft
Unlike traditional credential theft, modern phishing kits focus on capturing and replaying active session tokens. Huntress highlighted three primary tradecraft techniques used by these kits:
- Device Code Phishing: Victims authenticate directly with an identity provider while attackers capture the resulting authorization, reducing user friction because no unfamiliar login page is used.
- Adversary-in-the-Middle (AiTM): Threat actors relay authentication flows in real time using fake login pages or intercepted exchanges, capturing session data even after successful MFA completion.
- Token Replay: Attackers reuse stolen sign-in tokens to access cloud resources and email accounts instantly.
Analyzed Phishing Kits
In recent months, researchers analyzed three notable phishing kits targeting Microsoft 365:
- EvilTokens: Discovered in early 2026 during a device code phishing campaign abusing the Railway Platform-as-a-Service, later linked to an operator arrest following a joint effort by Microsoft's Digital Crimes Unit and the FBI.
- Knight Office: An AiTM phishing kit that steals valid Microsoft 365 session tokens, feeds them into an operator console, and enables persistence across tenant accounts.
- Kali365: A Phishing-as-a-Service (PhaaS) operation bundled into a control panel that captures tokens through device code flows and reverse-proxy lures, featuring built-in AI capabilities to scale activity.
Practical Defensive Implications and Verification
Defenders investigating identity compromise must look beyond the initial phishing page to examine the entire attack sequence, from the lure to token issuance and mailbox activity.
- Detection Steps: Check for successful sign-ins from unfamiliar cloud infrastructure, hunt for device code authentication, review automated token refreshes, and inspect new devices and authentication methods.
- Containment Priorities: Revoke refresh tokens, remove unauthorized devices and Windows Hello credentials, restrict device code authentication where possible, and investigate mailbox access and forwarding rules.
To verify original announcements and research findings, security professionals can consult official reports published by Huntress and security advisories from Microsoft.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Microsoft Calls Copilot 'The New OS for Work' at Ignite Keynote, Bringing Office Apps Inside the AI
 Critical Microsoft Authenticator Flaw Allowed Android Apps to Steal Session Tokens
 Working Alongside Code: Inside the Rise of AI Agents in Modern Workplaces
 NordVPN Warns of Malicious GTA 6 PC 'Scam Kits' Sold on Dark Web