Navigating Bug Bounties and Cybersecurity Learning in the AI Era
· GlobeWire Daily Editorial Desk · Source: www.bleepingcomputer.com
Image: www.bleepingcomputer.com
The Changing Landscape of Bug Bounties
Learning cybersecurity with the goal of finding real security flaws and participating in bug bounty programs has become increasingly complex. While these programs allow individuals to test skills on real software and help developers improve safety, recent industry developments highlight shifting trends in submission quality and program availability.
According to reported accounts from maintainers, the rise of automated tools has occasionally flooded programs with low-quality or speculative reports. For instance, the data transfer tool curl temporarily ended its paid bounty program in early 2026 due to a deterioration in submission quality, noting that confirmed vulnerability rates dropped significantly before later recovering as submission dynamics shifted. Other organizations have similarly adjusted or paused specific scopes of their vulnerability reward programs while maintaining broader operations.
Practical Foundations for Beginners
For those starting out in cybersecurity, these industry shifts emphasize the importance of rigorous, evidence-based reporting. Key foundational steps include:
- Understanding Core Systems: Learning how HTTP requests, login sessions, permissions, and application data handling work.
- Developing Technical Literacy: Gaining basic networking and command-line skills to investigate unexpected tool outputs.
- Practicing in Safe Environments: Using dedicated learning platforms, such as browser-based labs, to test concepts without impacting live services.
Building Reproducible Reports
A central lesson for aspiring bug hunters is taking full responsibility for the evidence behind any security claim. Generating an automated report is significantly easier than proving whether a vulnerability genuinely holds up under review.
Before submitting findings to any authorized program, best practices dictate including:
- Confirmation that the affected asset and testing fall within scope.
- Exact setup instructions and reproduction steps.
- Supported evidence, such as requests and responses, with sensitive data redacted.
- Clearly identified security impacts, separating proven behavior from untested assumptions.
Suggested Verification Steps
To verify announcements and learn more about safe vulnerability disclosure, interested individuals should consult official platform rules, maintainer advisories, and structured educational roadmaps directly through verified cybersecurity training providers.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Chainalysis Discloses Data Breach Involving 'Offensive Agentic Techniques'
 New 'Volta-Autodoxer' Infostealer Integrates Artificial Intelligence to Profile Victims
 CISA Adds Ivanti Connect Secure Flaws to KEV Catalog Following Active Exploit Chain
 Cloudflare reports 38% rise in network‑layer DDoS attacks in Q3 2026, driven by short‑burst booter services
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 South Africa Overtakes Australia to Top ICC Test Rankings After 2‑1 Series Win in Cape Town
 Pakistan Prime Minister Faces Social Media Scrutiny Following Hong Kong Sixes Win
 Open‑Source ‘It’s a Plan’ Offers Self‑Hosted Project Management with AI Agents
 Delhi Cyber Cell Investigates High School Student Over 17 Lakh Life Certificate Fraud APK
 South Africa Seal Test Series Against Australia in Cape Town
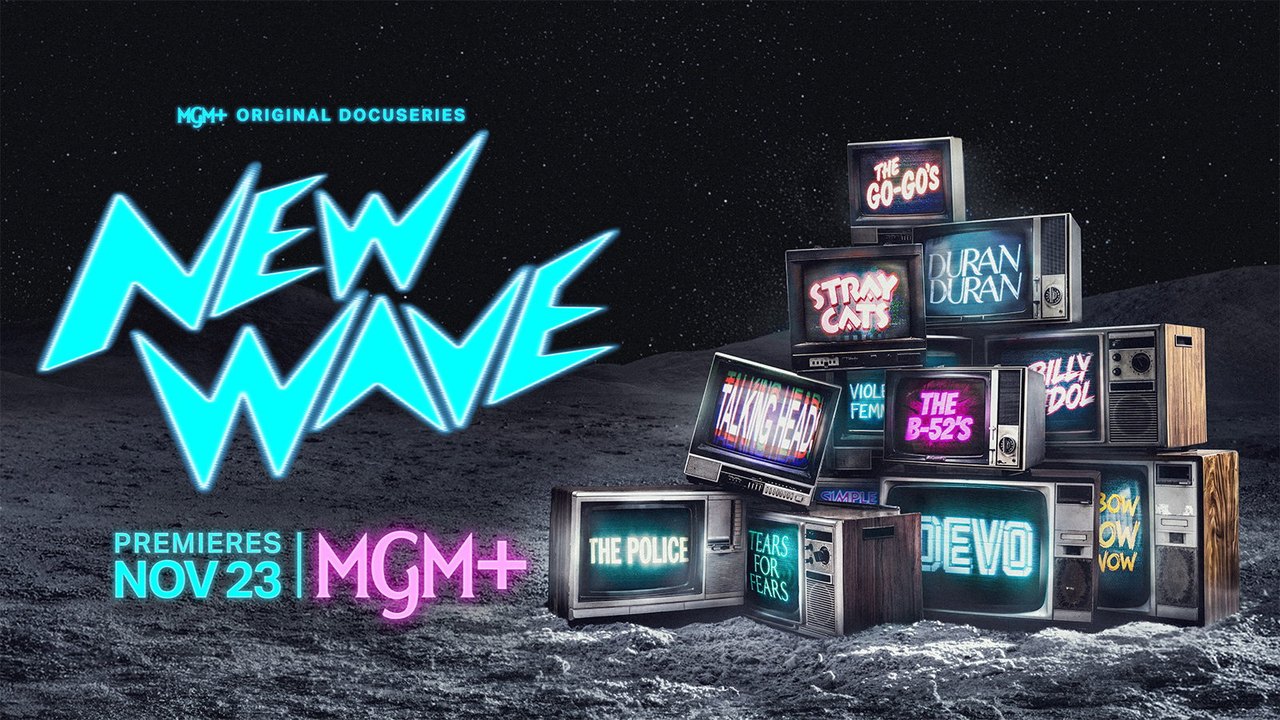 MGM+ Announces Four-Part Documentary Series 'New Wave' Detailing Music Evolution from 1977 to 1987