NSE Highlights Broker Lapses in Margin Trading, Client Funds, and Cybersecurity
· GlobeWire Daily Editorial Desk · Source: www.business-standard.com
Original GlobeWire Daily editorial illustration — not an event photograph.
Overview of NSE Inspections
The National Stock Exchange (NSE) has highlighted multiple compliance failures among stockbrokers following recent inspections covering the period from October 2025 to March of the current year. According to the exchange's circular, the identified issues span across margin trading facilities (MTF), client fund management, operational controls, authorised person conduct, and cybersecurity measures.
Key Compliance Lapses Identified
The regulatory review brought to light several operational and financial irregularities:
- Margin Trading Facility (MTF): Certain brokers reportedly failed to collect adequate margins—such as cash, cash equivalents, or Group I equity shares—with proper haircuts. Additionally, MTF was extended against ineligible securities outside the Group I category.
- Client Fund Handling: Observations noted instances of payouts exceeding available credit balances, delayed settlement of client funds, and failure to upstream clear credit balances to clearing corporations on time. Reports also indicated the improper pledging of fully paid-up securities, invocation of securities exceeding debit balances, and passing on short-collection penalties to clients.
- Authorised Persons (APs): Lapses included APs directly accepting funds from or making payments to clients, accessing client user IDs and passwords to trade on their behalf, promising assured returns, mis-selling products, and running unauthorised portfolio management services.
- Operational and Reporting Deficiencies: Trading terminals were occasionally found missing from reported locations. Other reported issues involved incorrect data submissions under risk-based supervision and annual returns, delayed contract notes, trading in minor accounts, and inadequate client surveillance.
Cybersecurity Vulnerabilities
The exchange's cybersecurity review pointed out critical technical shortcomings in broker infrastructure:
- Absence of two-factor authentication (2FA) or validation on critical systems.
- Inadequate password policies and lack of encryption for data at rest.
- Use of generic user IDs with privileged access.
- Lack of web application firewalls (WAF) for internet-facing infrastructure.
Practical Implications and Verification
The NSE has advised all member brokers to reinforce their internal compliance systems, upgrade technical controls, and rectify the observed procedural gaps. Market participants and investors can review official circulars published directly on the NSE website to verify regulatory guidelines and compliance frameworks.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Mistral Releases Trillion-Parameter 'Le Chonk' AI Model for Cybersecurity
 IANS Integrates Practitioner-Validated Cybersecurity Intelligence into Microsoft Copilot
 Google Announces Gemini 4 Carbon Model Highlighting AI Coding and Cybersecurity Claims
 Google Unveils Gemini 4 Carbon AI Model Emphasizing Cybersecurity and Coding Improvements
Related coverage
Related reporting available at publication.
Mistral Releases Trillion-Parameter 'Le Chonk' AI Model for CybersecurityIANS Integrates Practitioner-Validated Cybersecurity Intelligence into Microsoft CopilotGoogle Announces Gemini 4 Carbon Model Highlighting AI Coding and Cybersecurity ClaimsGoogle Unveils Gemini 4 Carbon AI Model Emphasizing Cybersecurity and Coding Improvements NewCore Wins 2026 Cyber Top Innovator Award for AI Agent Identity Governance
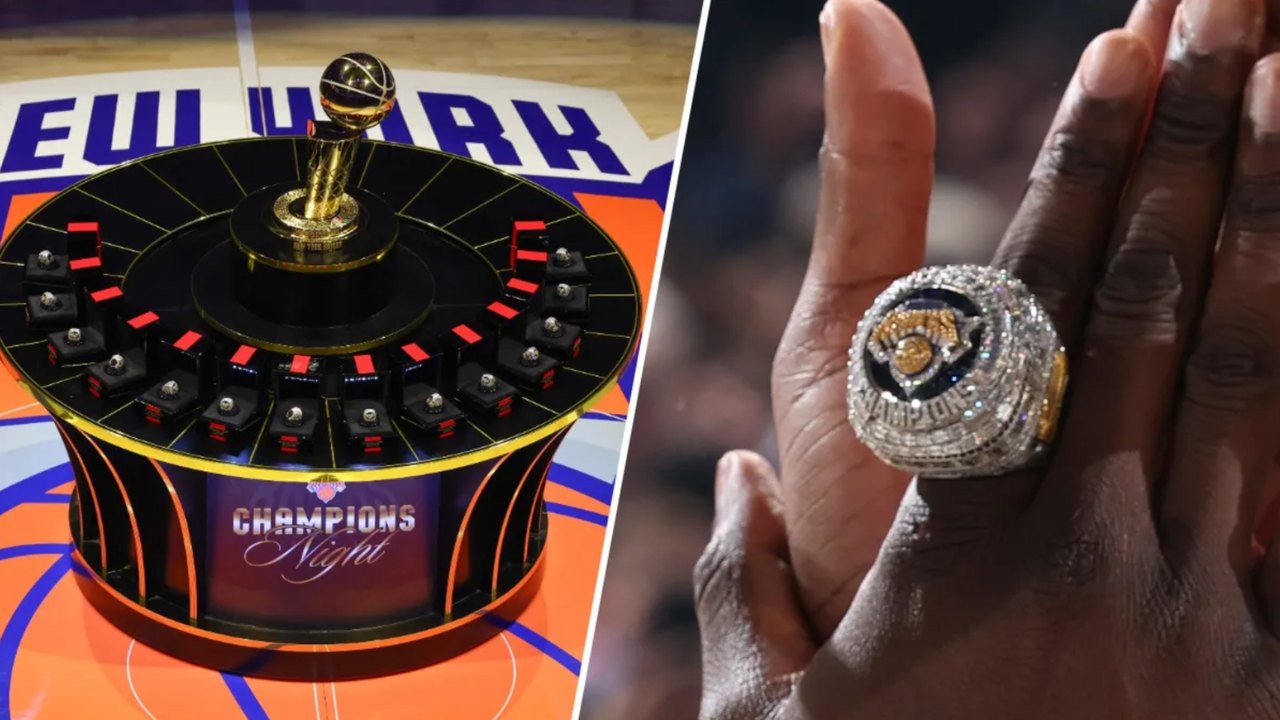 New York Knicks Face Criticism Over Phishing Test Disguised as Championship Ring Offer