Optimizely Supply Chain Attack Compromises Major Brand Websites With Malware
· GlobeWire Daily Editorial Desk · Source: www.bleepingcomputer.com
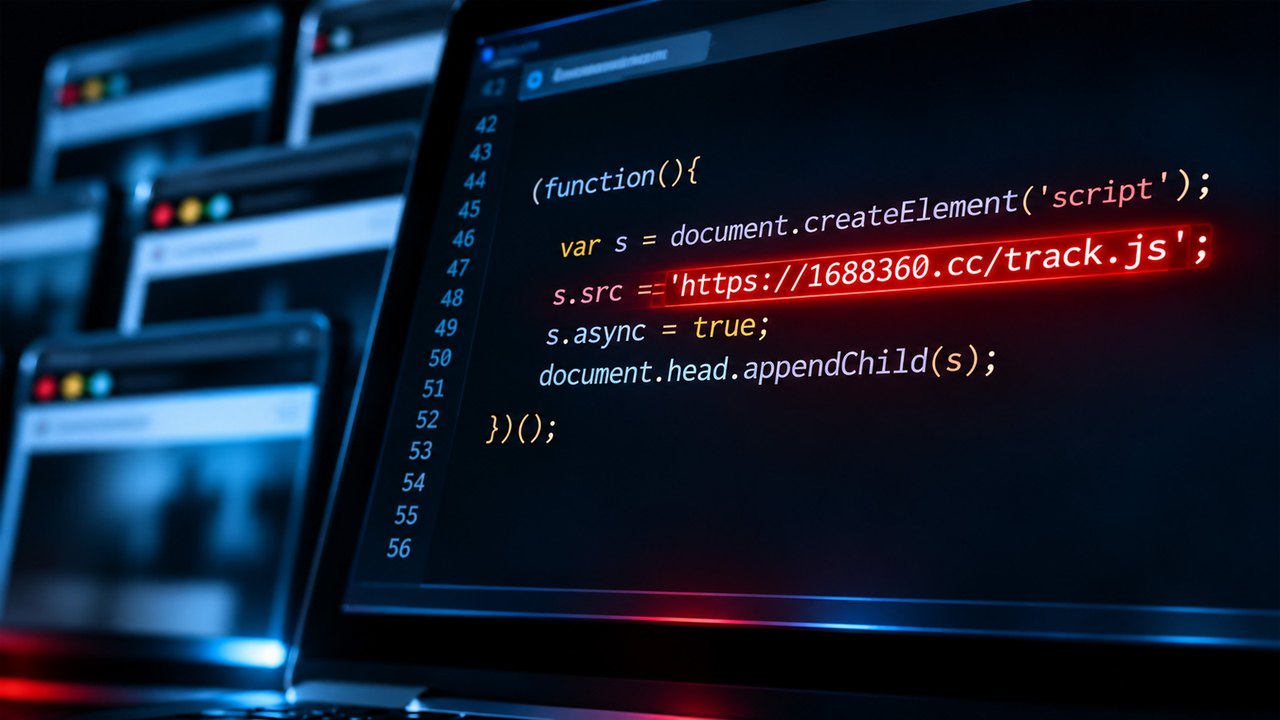
Image: BleepingComputer · Photo source · Resized and letterboxed to 16:9; no AI generation
A suspected supply chain attack targeting the digital experience platform Optimizely has resulted in malicious JavaScript being loaded on numerous popular websites, including Zoom, CNN, BBC, and Salesforce. Security researchers reported that the incident exposed visitors to scripts designed to steal cryptocurrency, skim payment information, and deliver exploits targeting iOS devices.
The incident was initially uncovered by security researcher Scott Helme, who reported that his team identified 188 infected Optimizely JavaScript files across 178 organizations after analyzing platform scripts. According to the analysis, malicious code was inserted into customer projects, causing scripts hosted on the company's content delivery network (CDN) to load malware.
Confirmation and Technical Details
Independent analysis confirmed that malicious scripts loaded or attempted to load on numerous affected sites. Technical investigations revealed that attackers injected code designed to retrieve an additional script from an external server. The injected payload utilized various obfuscation techniques, including direct referencing and Base64 encoding.
Key capabilities identified in the malicious track.js file include:
- Cryptocurrency Hijacking: Monitors webpage elements for cryptocurrency wallet addresses and replaces them with attacker-controlled destinations to intercept transfers.
- Payment Card Skimming: Searches for credit card numbers, expiration dates, and security codes entered by users, attempting to exfiltrate the data to external servers.
- iOS Exploit Delivery: Loads secondary payloads, such as the Coruna and DarkSword exploit kits, targeting Apple iPhones and iPads running specific versions.
- Data Collection: Gathers browser cookies, webpage URLs, and screenshots for transmission to unauthorized parties.
Helme's investigation noted that cryptocurrency wallets associated with the script received approximately $7,000 in transactions on November 16, indicating successful clipboard-hijacking activity.
Cleanup and Unknowns
Remediation efforts significantly reduced the count of compromised files, with only one of the previously flagged scripts containing malicious code by late November 16 UTC. While the earliest script hijacking was traced to the early morning hours of November 16, the exact vector remains undetermined.
It remains unknown how attackers gained authorization to modify customer projects. Investigators and observers have not confirmed whether the vector involved a broader compromise of Optimizely infrastructure, compromised credentials, or an alternative unauthorized access method. Verification of platform security advisories and direct platform status updates remain recommended for affected organizations.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Optimizely Supply Chain Attack Injects Malware into High-Profile Websites
 Major Supply-Chain Cyberattack Targets High-Traffic Websites via Optimizely
 Malicious Malware Cocktail Distributed Through Optimizely Infrastructure Affects Hundreds of Websites
 Cyberattack Targets iPhones and Crypto of Visitors to Major Websites