Ransomware Affiliates Deploy AI Agents in 'Phantom' Framework to Automate Intrusions, Researchers Find
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
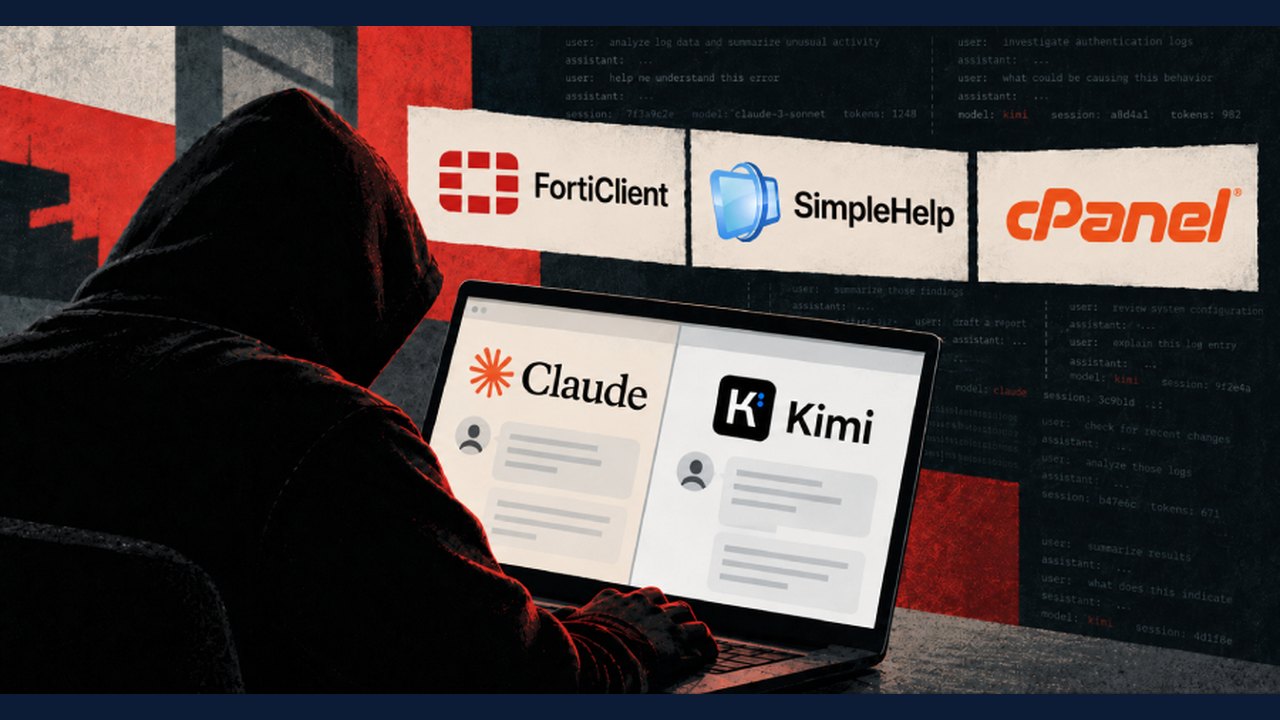
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Cybersecurity researchers at SOCRadar have uncovered an artificial intelligence-driven intrusion ecosystem operated by affiliates of the INC and The Gentlemen ransomware groups. The operation centers on an "Autonomous Red Team Kill Chain Framework" dubbed Phantom, which automates the full intrusion lifecycle while keeping a human operator in the loop for approval.
How the AI-Driven Operation Works
The threat actor, assessed to be Russian-speaking, functions both as an intrusion and data-extortion operator and as an infrastructure provider for partners across the ransomware ecosystem. According to SOCRadar, the operators exploited edge and remote-access systems at scale, including FortiClient EMS, SimpleHelp, cPanel, and VPN gateways. They used AI-managed knowledge bases to track victims, stolen credentials, and campaign progress.
A defining characteristic is the "AI-executed, human-approved operating structure": a human operator provides a victim-specific prompt and reviews every step, while the intrusions themselves are executed through OpenCode with OpenRouter-hosted commercial models. Analysis of an exposed directory at 45.227.254[.]43 revealed 8,257 messages logged across 133 sessions. When models refused to act on prompts, the operator rewrote requests as authorized red team assessments rather than switching models.
Exploited Vulnerabilities and Initial Access
Initial access is achieved by exploiting public-facing edge devices at scale. The attackers then move laterally, establish persistence, exfiltrate data, and escalate toward ransomware deployment. Operator records indicate exploitation of the following flaws:
- CVE-2024-57727 – SimpleHelp path traversal (actively exploited)
- CVE-2026-35616 – Fortinet FortiClient authentication bypass (actively exploited)
- CVE-2026-41940 – cPanel/WHM authentication bypass (actively exploited)
- CVE-2026-15409 – SonicWall SMA 1000 SSRF (staged for targeting, no confirmed compromise)
- CVE-2026-63030 – WordPress wp2shell (developed)
- CVE-2026-42208 – LiteLLM SQL injection (developed or referenced)
- CVE-2026-9082 – Drupal SQL injection (developed or referenced)
Once inside, the operators followed a recurring lifecycle: enumerate the domain, escalate to domain admin where possible, harvest credentials with stealer tooling, prioritize finance, HR, legal, and executive files, and collect them over reverse-SOCKS tunnels. Credential reuse was the main force multiplier; in one case, a single reused password unlocked the VPN, servers, RMM, backup, and security management platforms at once. Security products were impaired with a BYOVD killer and loader-level evasion, although the operators' own logs record mixed results against enterprise EDRs.
Toolkit: Phantom, Ghost C2, and Custom Malware
Supporting the threat actor is a diverse toolkit comprising bespoke frameworks, modified open-source tools, and compiled binaries:
- Phantom – An AI-powered offensive security and penetration testing framework deployed in live operations via OpenCode. It employs an agent that communicates with an external server to retrieve tasks, execute commands, and return outputs. It supports 18 skill modules for reconnaissance, binary reverse engineering, exploit research, steganography, telemetry assessment, and EDR fingerprinting.
- WormGPT-MCP – A set of 32 Model Context Protocol (MCP) servers connecting the AI system to modules spanning functions from reconnaissance to extortion.
- Ghost C2 – Three generations of polymorphic implants communicating with a remote server over Cloudflare, Telegram, or DNS, executing tasking and maintaining persistent beacons.
- RevSocks – A reverse SOCKS5 framework used to pivot inside victim networks and stage data for exfiltration.
- Other tools – A Cloudflare-fronted Mythic agent dubbed QuickLine, a Quick Heal/Seqrite EDR killer abusing the Zemana driver ("zam64.sys") as part of a BYOVD attack, and exfiltration programs such as rks3 and BackupAgent.
Extortion Tactics and Victim Profile
Analysis of dozens of AI-authored extortion records shows a data-centric approach. The threat actors examine stolen financials to determine the amount a victim can pay without involving a bank or insurer, then send masked proof samples and ramp up pressure through scripted vishing calls and threats to notify customers, partners, and regulators. Stolen data is published on the data leak site if the victim fails to pay within a 24–72 hour deadline. Final outcomes of these ransom demands are unknown; no cryptocurrency wallet or payment record has been recovered.
A total of 62 organizations are estimated to have been targeted, with four listed on the data leak sites for INC and The Gentlemen ransomware. The United States accounts for more than 50% of targets. Attacks primarily targeted industrial, manufacturing, and energy sectors, followed by healthcare and pharmaceutical organizations.
Practical Implications for Defenders
Organizations should prioritize patching the actively exploited vulnerabilities listed above, especially on internet-facing edge devices. Credential hygiene remains critical: enforce unique, complex passwords across all systems and implement phishing-resistant multi-factor authentication. Monitor for reverse-SOCKS tunnels and unusual outbound connections to Cloudflare, Telegram, or DNS channels associated with Ghost C2. Deploy EDR solutions with behavioral detection capable of identifying BYOVD attacks and driver abuse (e.g., zam64.sys).
How to Verify and Respond
SOCRadar's full technical report includes indicators of compromise, YARA rules, and MITRE ATT&CK mappings. Security teams should review the report directly at the source URL, correlate IOCs with internal telemetry, and engage incident response providers if compromise is suspected. The exposed infrastructure at 45.227.254[.]43 has been documented; defenders can block this IP and monitor for related traffic.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Open-Source AiSOC Launches to Automate Threat Triage With Auditable AI Agents
 Open‑source toolkit offers evidence‑based steps to recover DSM ransomware‑encrypted data
 Higgsfield AI Launches Markdown-Based Skill Set for Visual Brand Agents
 nodeterm Introduces Spatial Terminal Manager for AI Coding Agents Across Desktop, Browser, and Mobile
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 A Guide to Understanding UK Housing and Local Authority Services
 Open Source Community Launches New Home for Papers with CodeHiggsfield AI Launches Markdown-Based Skill Set for Visual Brand Agentsnodeterm Introduces Spatial Terminal Manager for AI Coding Agents Across Desktop, Browser, and MobileOpen‑source toolkit offers evidence‑based steps to recover DSM ransomware‑encrypted data
 Government Guidance on Environmental and Rural Land Management in England