Security Experts Report Spike in Ransomware Attacks Linked to AI and Emerging Groups
· GlobeWire Daily Editorial Desk · Source: www.wired.com
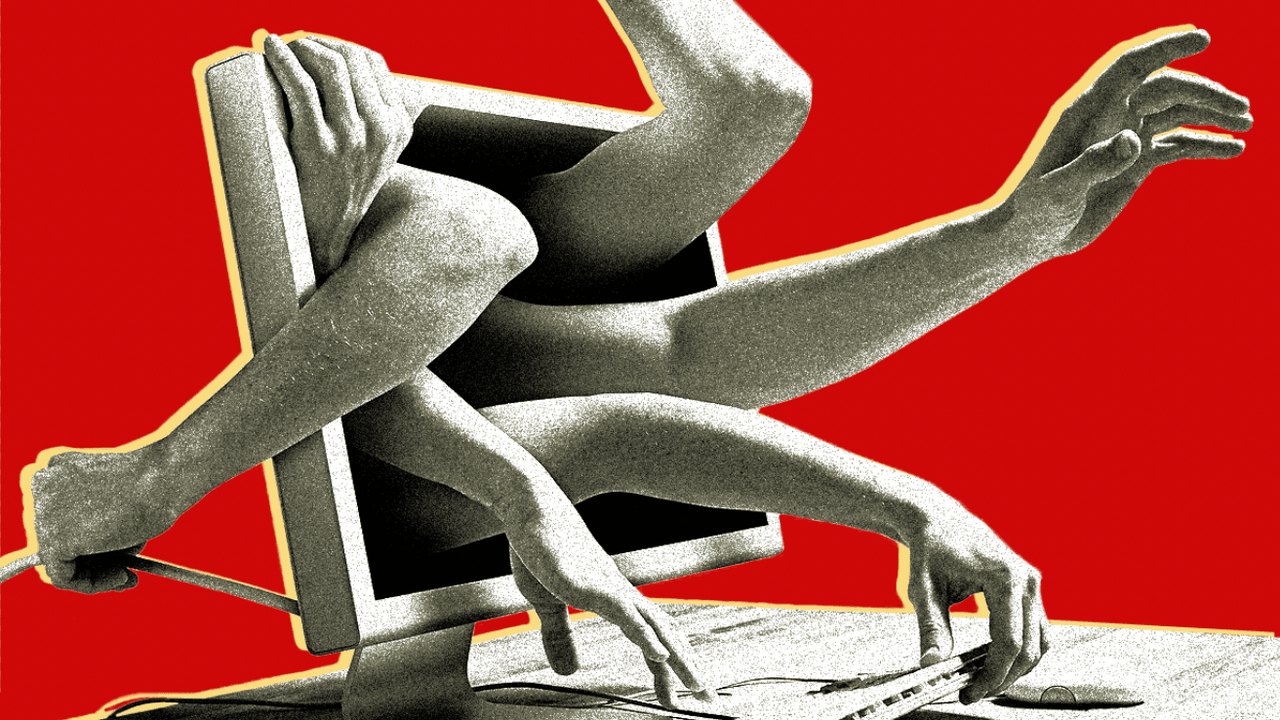
Image: Matt Burgess · Photo source · Resized and letterboxed to 16:9; no AI generation
Cybersecurity researchers report that ransomware and data extortion attacks have increased globally, with experts pointing to artificial intelligence as a contributing factor in how threat actors scale operations. While fully autonomous AI-driven attacks have not yet emerged, analysts note that criminals are utilizing large language models for tasks such as phishing emails and extortion negotiations.
Key Findings from Researchers
- Spike in Claims: Security firms note that alleged attacks posted on leak sites reached nearly 3,000 incidents over the summer, representing an estimated 20 to 40 percent increase from the spring.
- Rise of New Groups: Fragmentation within the ecosystem has led to numerous small or independent operations. Halcyon analysis indicates roughly 111 ransomware groups made claims between July and September.
- AI and Phishing: Experts from Recorded Future and Halcyon observe that AI helps lower barriers to entry, enabling inexperienced operators to launch independent schemes, improve scam content, and exploit vulnerabilities.
- Shift Toward Data Extortion: While traditional groups use double extortion (encrypting systems and stealing data), newer independent actors may focus purely on data exfiltration to simplify operations.
Practical Implications and Verification
Organizations face increased uncertainty as the number of claimed attacks outpaces the ability to immediately verify every incident. Security professionals recommend reviewing access controls, monitoring for phishing indicators, and relying on threat intelligence reports from established cybersecurity firms to verify trends and specific advisories. This overview is based on reported observations from security researchers and industry publications.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 US Tech Outages Stem From Economic Incentives Rather Than Cyber-Attacks, Security Expert Argues
 Keeper Security Launches Global Emergency Breach Response Service for Active Cyber Attacks
 Bollywood Faces Renewed Security Concerns Amid String of Attacks
 US Senators Warn White House of Advancing AI Cyber Threats as GAO Reports Security Risks