SilentAir Group Compromises Asian Telecom Networks for SMS Interception
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
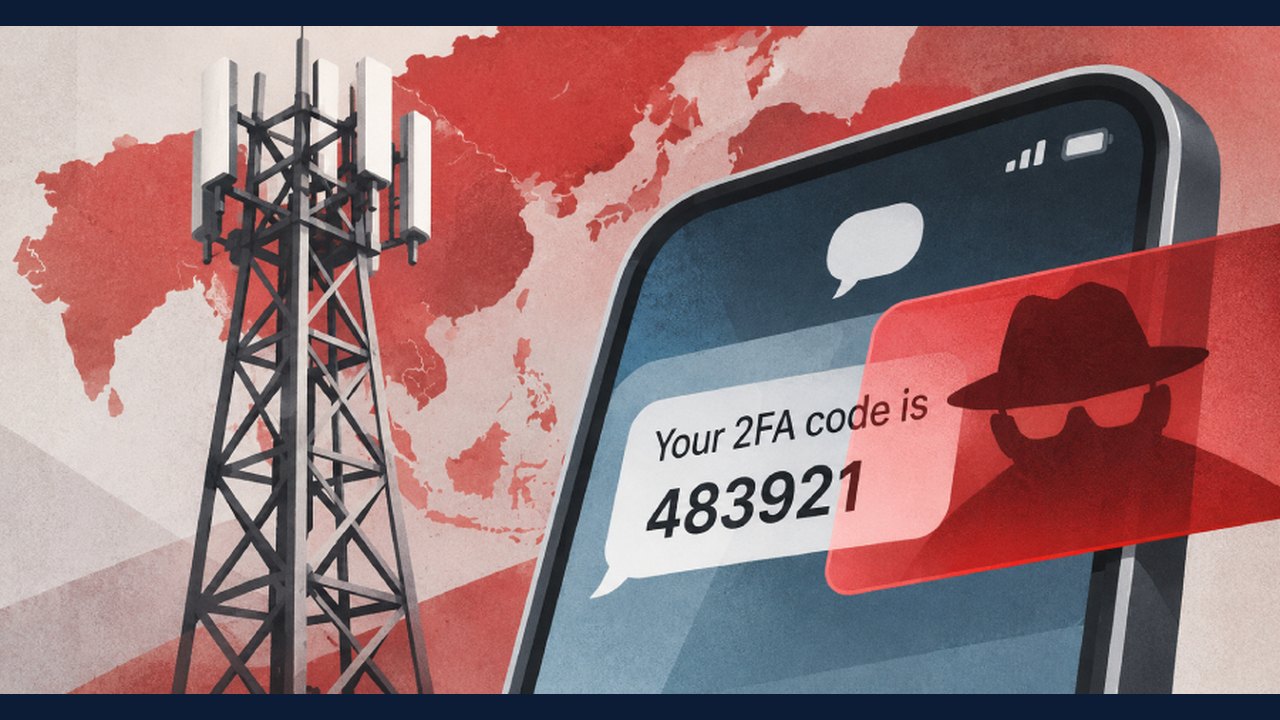
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Overview of SilentAir
Security firm Enea has identified a sophisticated threat actor, dubbed 'SilentAir,' which has successfully compromised infrastructure within Asian mobile operators. The group uses hacked equipment to intercept signaling traffic, specifically targeting calls and text messages, with a heavy focus on users in Taiwan.
Attack Mechanism
SilentAir exploits the trust inherent in the SS7 and Diameter signaling protocols—the backbone of global roaming and mobile connectivity. By injecting unauthorized 'UpdateLocation' messages into the shared IPX network, the group misdirects traffic intended for a target’s phone to attacker-controlled equipment.
Key observations regarding their tactics include:
- SMS Interception: The group successfully captured two-factor authentication (2FA) codes in several instances.
- Silent SMS: Attackers deployed large volumes of 'silent' text messages—which do not trigger user notifications—to verify if the traffic interception was active.
- Operational Pattern: Attacks often followed a UTC+8 time cycle, leading researchers to suggest a potential regional origin, though a definitive state link remains unconfirmed.
Security Implications
The report highlights that SilentAir differs from typical surveillance entities by prioritizing interception over mere metadata collection. Enea notes that while the group’s activity has been currently disrupted, the underlying vulnerabilities in telecom signaling remain a significant risk.
Recommendations for Operators
Enea advises telecom providers to bolster their defenses beyond standard industry guidelines:
- Implement firewalls for both GTP-C and GTP-U protocols.
- Integrate signaling security monitoring with broader enterprise IT threat detection.
- Deploy internal network sensors to detect anomalous signaling traffic originating from within the operator's own infrastructure.
Consumers are currently advised that there are no specific individual remediation steps provided, as the compromise occurs at the network signaling layer rather than the device level.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Samsung, SK Telecom, and Hana Financial Group Deploy Korea's First Private 5G Smart Office
 Samsung to Deploy AI‑RAN Private 5G Networks for KT and SK Telecom Starting Oct 2026
 TRAI Releases Draft Guidelines on Responsible AI Use in Telecom Networks
 MTN Group Enters Early Discussions to Acquire Rival Telkom SA in Cash-and-Stock Deal