OpenCode Console Breach Reportedly May Have Exposed Third-Party AI Provider Keys
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
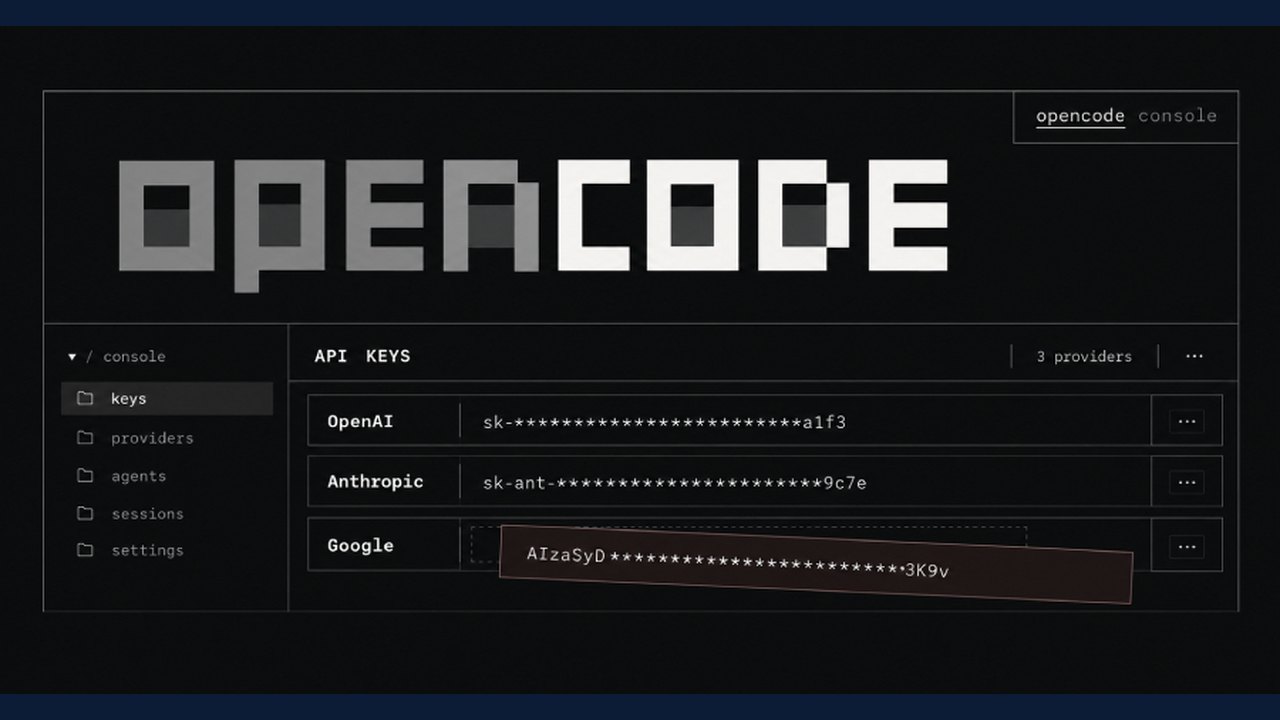
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
OpenCode reported an unauthorized intrusion into a legacy system on the night of October 16, which may have exposed third-party AI provider keys saved by users in the OpenCode Console. OpenCode stated that the incident affected 1.4% of Console users who had linked outside provider keys.
Incident Details and Scope
OpenCode distributed an email to affected users on the morning of October 17 titled "Action Required: Potential provider key breach." Co-founder Dax Raad clarified on X that the breach involved the OpenCode Console service rather than the core OpenCode application, noting that keys added locally to command-line and desktop apps are stored separately in a SQLite database.
OpenCode characterized the situation as ongoing on October 17, stating it was working with OpenAI, Anthropic, and Google, and described the event as "related to a large-scale distillation attack." The company has not publicly disclosed the total number of keys held, the exact number of users represented by the 1.4% figure, when the unauthorized access started, or the specific mechanics of how the legacy system was reached.
Potential Risks and User Impacts
Provider keys function as bearer credentials, allowing anyone with a copy to execute billable requests against an owner's account until revoked. OpenCode noted that deleting a compromised key from Console does not automatically revoke it with the provider.
- Reported Financial Losses: Multiple users have reported unexpected charges on their accounts. Publications such as Dealroom and Notebookcheck cited user statements on social media and Reddit detailing unauthorized usage fees ranging from hundreds of dollars or euros across OpenAI, Anthropic, and Google accounts.
- OpenCode's Stance: OpenCode has officially stated that keys "may have been exposed," but has not explicitly confirmed whether any keys were definitively copied or actively used by the intruder.
Recommended Verification and Remediation Steps
OpenCode and provider guidelines recommend the following actions for affected individuals:
- Revoke compromised keys directly within the respective OpenAI, Anthropic, or Google dashboards and generate new credentials.
- Update all applications and scripts relying on the previous keys.
- Review account usage and billing histories dating back to October 16 for unfamiliar activity.
- Configure spend limits and alerts, and assign unique keys to individual tools to limit future exposure.
Users can verify official announcements by checking OpenCode's verified social media channels or reviewing direct communications received via email.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Japan Airlines Discloses Third-Party Data Breach Affecting 92,000 Customers
 Law Firm Probes BCD Travel Data Breach Following Third-Party Cyber Attack
 Amazon CEO Andy Jassy Says Third-Party AI Shopping Assistants 'Not Great' Yet
 DoorDash Reports Only 'Several Hundred' Orders From Third-Party AI Agents
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 Madhya Pradesh Government Plans Revenue Generation from 117-Year-Old Edward Villa in Mumbai Through Leasing
 iPhone 18 Pro Named TechRadar Product of the Year 2026
 Google Project Suncatcher Runs Gemma 4 AI on Orbiting Satellite and Receives First Response
 Gender Disparities in Eye Care Access Across India Examined
 Satellite Images Show Cyclone Arnab Weakening Over India As New System Brews
 Expanding Green and Blue Spaces Crucial for India's Economic and Public Health, Reports Indicate