Over 26,000 Active AI and Cloud Credentials Exposed on Gitee
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
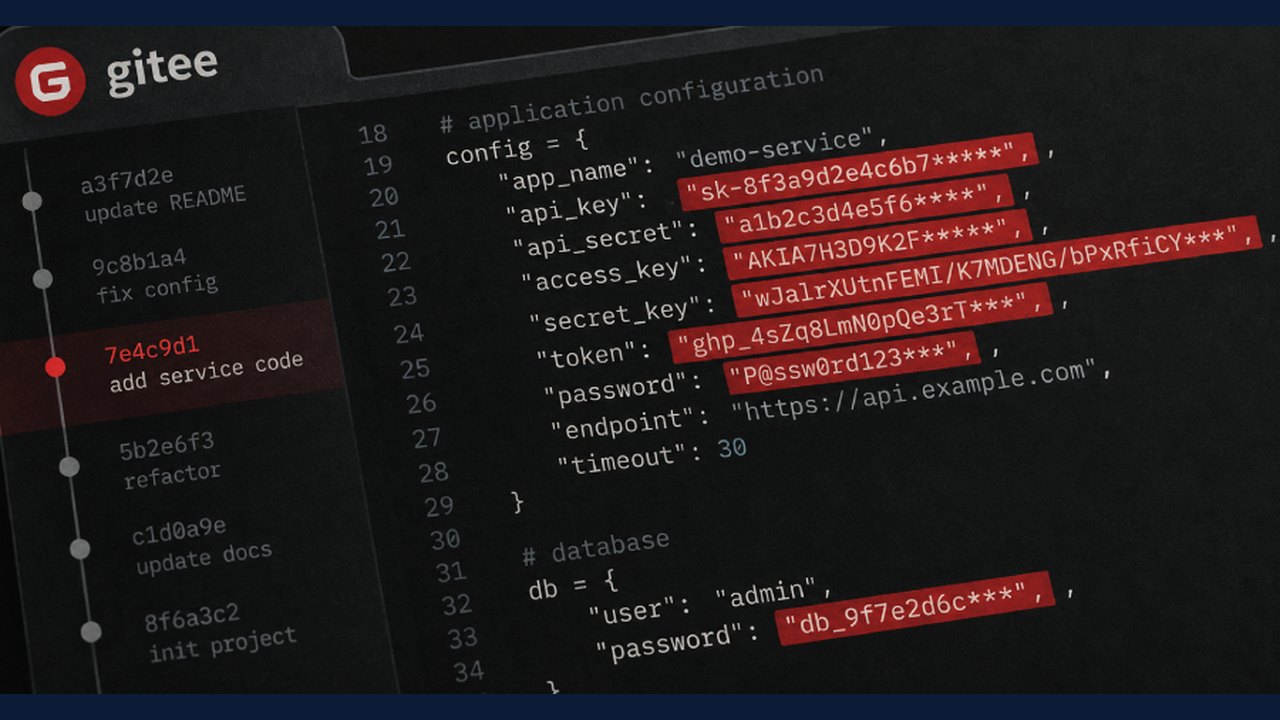
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Security Vulnerability Report
A recent security analysis of 7.25 million public repositories on the Chinese code-hosting platform Gitee has revealed that 26,400 cloud and AI service credentials remain active. Independent researcher Ben Zimmermann conducted the scan, which utilized two secret-scanning tools: TruffleHog and Kingfisher.
Key Findings
- Total Active Credentials: 26,400.
- Major Sources: The largest group included 9,473 Alibaba Cloud AccessKey pairs, followed by 3,805 YouTube API keys, 3,170 DeepSeek keys, 1,489 Zhipu BigModel keys, and 1,348 OpenAI keys.
- Temporal Data: Nearly half of the compromised credentials (12,242) were introduced in 2025, though some dated back to the late 2000s.
The Risks of Exposed Keys
Exposing an API key can lead to significant operational risks, including unauthorized charges, data loss, and depletion of service quotas. The researcher noted that even if a key is removed from a repository's current code, it remains valid if found in the repository's commit history. Deleting code does not revoke access; users must actively rotate keys through the service provider's management console.
Mitigation and Verification
Security experts and service providers recommend the following steps for those who may have pushed keys to public platforms:
- Revoke and Rotate: Immediately invalidate compromised keys at the provider level and issue new ones.
- Apply Restrictions: Implement API-level restrictions to ensure keys function only with necessary services.
- Monitor Logs: Review audit logs (e.g., Alibaba Cloud's ActionTrail) for unauthorized API calls or unexpected resource changes.
- Tooling: Developers should verify that their secret-scanning tools adequately cover all services utilized in their infrastructure, as the study found significant overlap gaps between TruffleHog and Kingfisher.
It remains unclear if any of the exposed credentials were exploited by malicious actors prior to the researcher's discovery. Users are advised to assume any key pushed to a public repository is compromised.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 A Pragmatic Playbook for Building Profitable AI Applications in 2026
 Asymptote Labs Releases Beacon: Open-Source Cross-Harness Memory Layer for AI Coding Agents
 Navigating the Risks: The Challenges Facing the Global AI and Tech Landscape
 Canada Launches $2M Challenge for AI Governance Tools That Track Decisions and Ensure Compliance
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 BMW G310R: Motorcycle Specifications, Facts and Verification Guide
 Yamaha FZR400: Motorcycle Specifications, Facts and Verification Guide
 Maxus EV30: Car Specifications, Facts and Verification Guide
 Forthing T5 EVO: Car Specifications, Facts and Verification Guide
 Huawei Mate 60: Smartphone Specifications, Facts and Verification Guide
 Redmi K70: Smartphone Specifications, Facts and Verification Guide