Brotli Decoder Vulnerability Impacts Node.js, Bun, Python, .NET, and Other Software
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
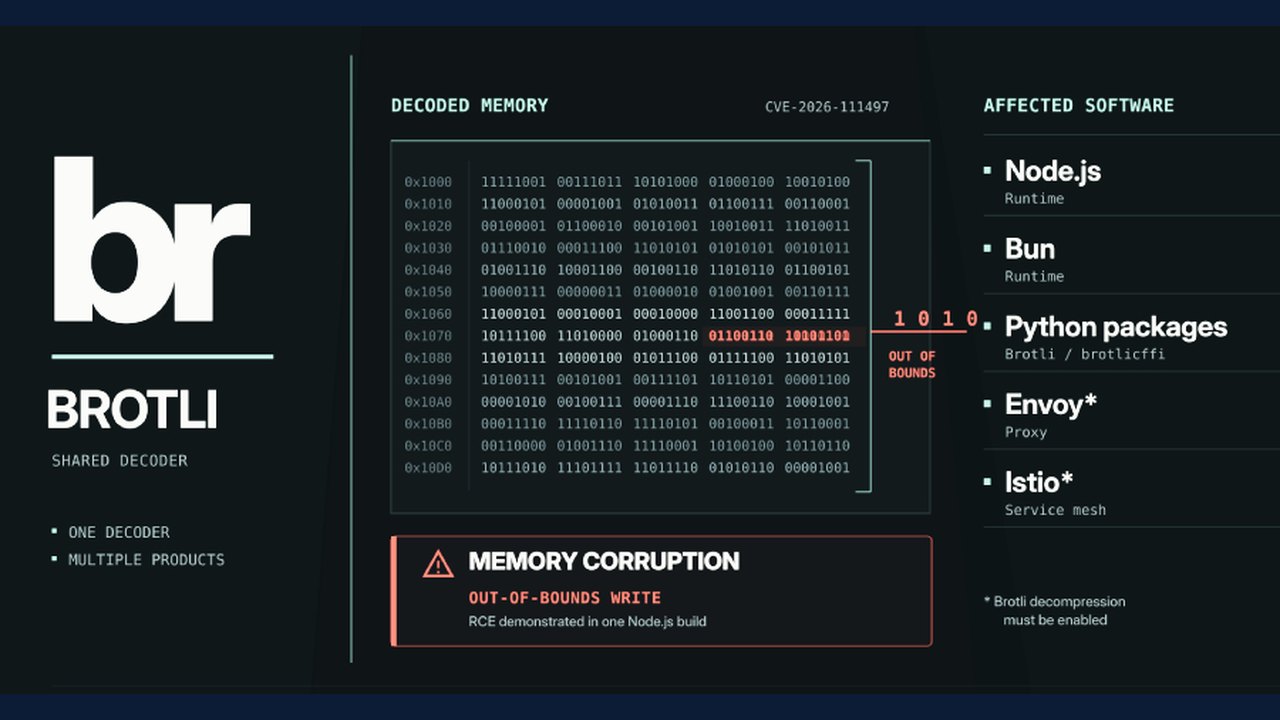
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Overview of CVE-2026-111497
A memory-corruption vulnerability in Google's Brotli compression decoder (tracked as CVE-2026-111497) affects multiple software ecosystems, including Node.js, Bun, Microsoft's .NET, Python packages, Envoy proxies, FFmpeg, ClickHouse, and Apache Arrow. The flaw arises from how the C code unpacks Brotli streams. If a program decodes attacker-controlled Brotli-compressed data, crafted payloads can cause a buffer overflow, potentially resulting in crashes, memory leaks, or remote code execution.
OpenAI's Codex Security team reported the issue, and Google assigned a CVSS score of 9.2 (critical). Other maintainers, including Red Hat and Microsoft, rate it between 8.1 (high) and important. According to available assessments, no in-the-wild exploitation has been publicly confirmed.
Affected Software and Exposure Vectors
Because various platforms bundle or reference their own copies of Google's decoder, they must be updated independently:
- Node.js and Bun: Exposed when built-in `fetch()` clients read Brotli responses (`Content-Encoding: br`) or when request-body parsers (such as Express 5) unpack incoming uploads.
- Python: Packages like `Brotli` and `brotlicffi` leave HTTP clients (`requests`, `httpx`, `urllib3`, `aiohttp`) vulnerable upon installation, even if an application never explicitly imports Brotli.
- .NET: Microsoft released out-of-band updates on October 25 for .NET 8, 9, and 10. Apps are exposed only if they use explicit Brotli APIs (`BrotliStream`) or enable automatic decompression.
- Other Systems: JFrog research identified vectors in FFmpeg (via libjxl metadata parsing), ClickHouse (handling HTTP requests, `.br` files, and Parquet data), and Apache Arrow.
Mitigation and Verification
Security advisories recommend the following verification and remediation steps:
- Update Runtimes and Libraries: Apply patches provided by vendors (such as updating Node.js, .NET runtimes, or Linux distribution packages). Restart running services and rebuild container images, as active processes retain the old decoder in memory.
- Disable Untrusted Decoding: Where updates are not yet available, reject incoming requests with `Content-Encoding: br` at the network edge, disable automatic client decompression, or uninstall unused Python Brotli bindings.
- Review Security Scanners: Automated dependency checkers may lag behind CVE records for Python packages or bundled libraries; administrators should manually verify installed versions.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Software Experts Recognizes Nicely Network as Top B2B SaaS Reddit Marketing Agency
 Tech Hiring Surges in Chennai as Flex Opens Associate Software Engineer Roles
 Associate QA Engineer – Software at Light & Wonder, Bengaluru – Join the Gaming Quality Team
 Saatvik Agro Announces Hiring for Analyst Software Engineer (Java) in Morena
Related coverage
Related reporting available at publication.
Software Experts Recognizes Nicely Network as Top B2B SaaS Reddit Marketing AgencyTech Hiring Surges in Chennai as Flex Opens Associate Software Engineer RolesAssociate QA Engineer – Software at Light & Wonder, Bengaluru – Join the Gaming Quality TeamSaatvik Agro Announces Hiring for Analyst Software Engineer (Java) in Morena Apple Intelligence Set to Arrive in China with Upcoming iOS 27.3 Beta
 Android 17 QPR3 Beta 3 Rolls Out with 26 Pixel Bug Fixes