CyberStrikeAI and Other AI-Driven Campaigns Target Global Infrastructure
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
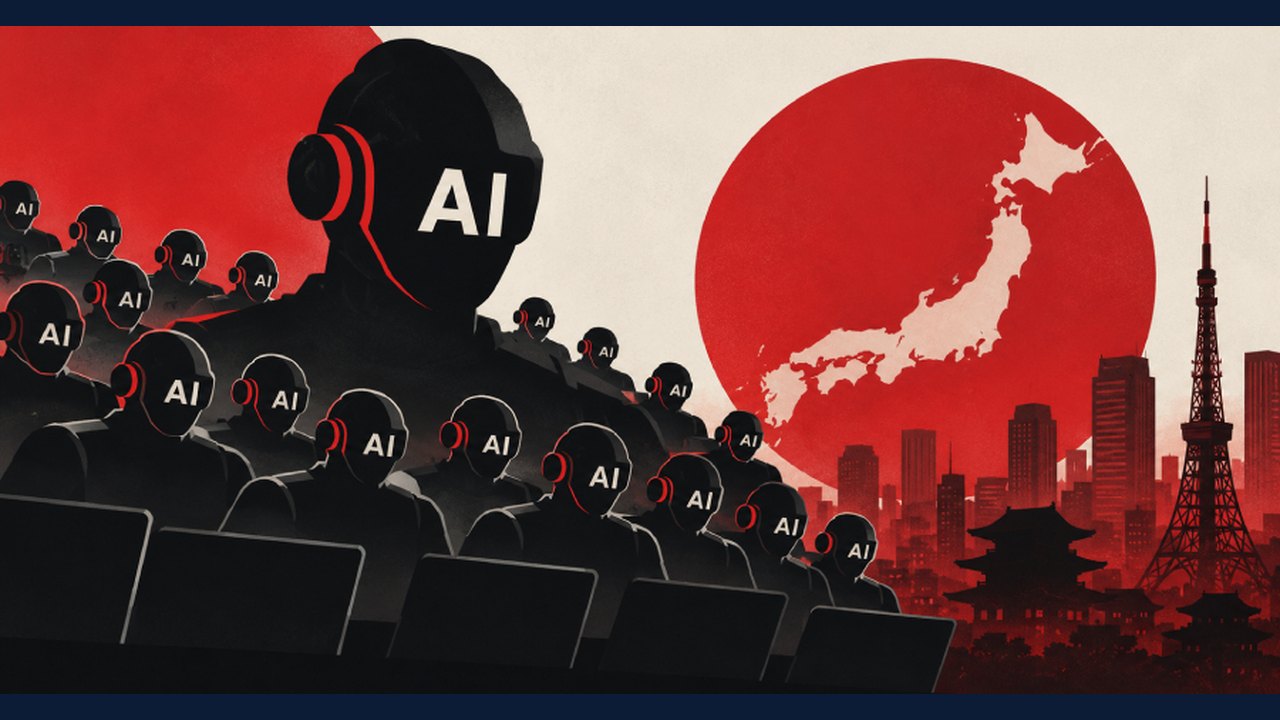
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Escalating AI-Integrated Cyber Threats
Cybersecurity researchers have identified multiple recent campaigns where threat actors are deploying agentic AI to automate various stages of the cyberattack lifecycle. Among the most notable findings is the use of 'CyberStrikeAI,' a framework that utilizes a swarm of 44 AI agents to handle tasks ranging from reconnaissance to data exfiltration and automated reporting.
Key Findings
- Automated Workflow: In attacks targeting Japan, CyberStrikeAI was observed managing the entire attack lifecycle, including generating Japanese-language phishing pages and fake login portals.
- Diverse Tactics: While some attackers use fully automated agentic systems, others rely on Large Language Models (LLMs) to accelerate manual tasks like script writing and reconnaissance.
- Global Reach: These campaigns are not localized; while Japanese entities were prime targets in recent incidents, similar methodologies have been observed impacting organizations in the U.K., France, Italy, Taiwan, Hong Kong, and across Latin America.
- Industrialized Attacks: AI is being used to industrialize existing methods, such as brute-forcing credentials, scanning for vulnerabilities in edge devices (e.g., Cisco, Citrix), and exploiting misconfigured cloud services.
Practical Implications
According to industry reports, the time between the discovery of a vulnerability and its weaponization has significantly decreased, in some cases falling below 24 hours. The integration of AI allows bad actors to operate with greater speed, scale, and autonomy, effectively acting as a 'force multiplier.'
Security teams are encouraged to prioritize the hardening of edge devices, the rotation of API tokens, and the continuous monitoring of cloud-based AI inference services to mitigate the risks posed by these autonomous toolsets. Organizations should verify the integrity of their network logs and ensure that administrative access remains strictly controlled.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 The Rising Threat of Operational Technology Hacking to Critical Global Infrastructure
 Global ESG Reporting Software Market Projected to Reach $4.48 Billion by 2031, Driven by Integrated Disclosures
 Global Anti-Data Center Movement Offers Lessons for US Communities Facing AI Infrastructure Boom
 Critical UEFI Firmware Flaw Threatens Global Server Infrastructure
Related coverage
Related reporting available at publication.
The Rising Threat of Operational Technology Hacking to Critical Global InfrastructureGlobal ESG Reporting Software Market Projected to Reach $4.48 Billion by 2031, Driven by Integrated DisclosuresGlobal Anti-Data Center Movement Offers Lessons for US Communities Facing AI Infrastructure BoomCritical UEFI Firmware Flaw Threatens Global Server Infrastructure Binance Halts Operations Following $6.3 Billion Cryptocurrency Heist
 Cisco Addresses Actively Exploited VPN Vulnerability in ASA and FTD Firewalls