Hotels Across Australia Impacted by Phishing Scam Following Booking Provider Data Breach
· GlobeWire Daily Editorial Desk · Source: www.abc.net.au
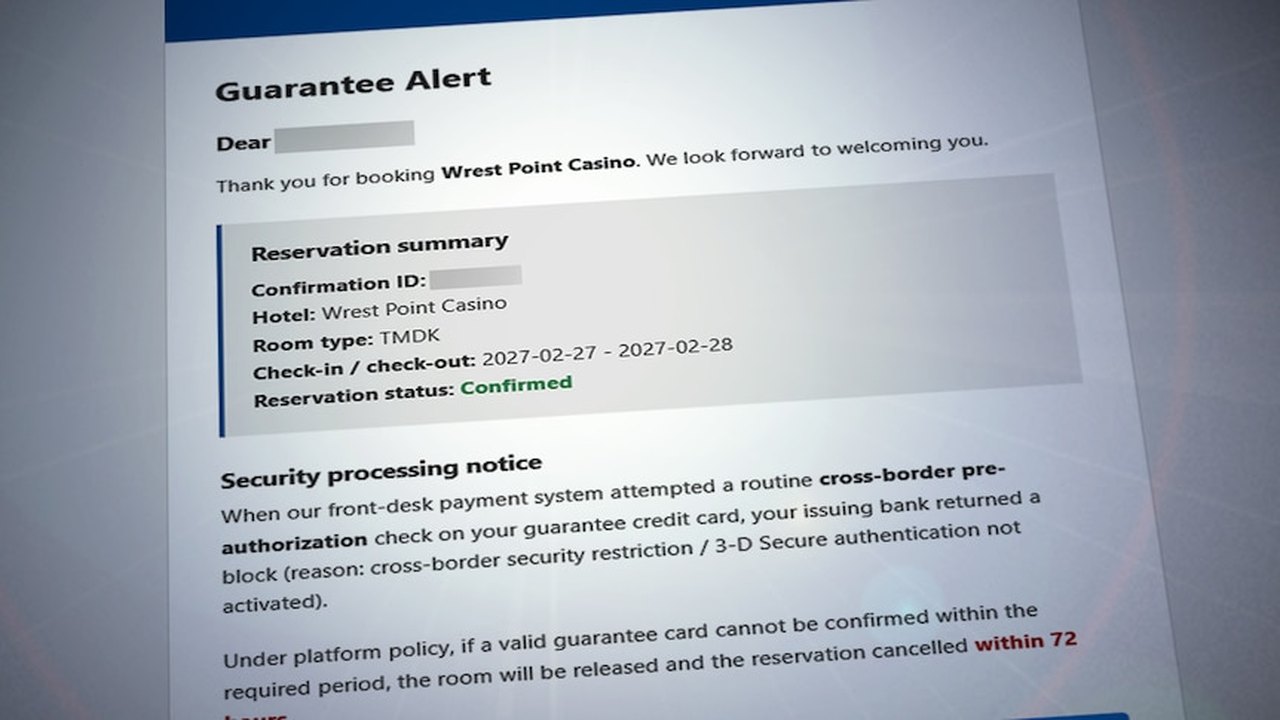
Image: www.abc.net.au · Photo source · Resized and letterboxed to 16:9; no AI generation
A data breach involving third-party booking provider RMS has affected multiple hotels across Tasmania and Australia, leading to sophisticated phishing scams targeting guests with accurate reservation details.
Reported on October 29, 2026, the incident involves guest names, contact information, and booking data being compromised. According to RMS, the stolen information has been utilized by bad actors to send convincing messages via email, text, and WhatsApp.
Details of the Phishing Scam
Guests at properties such as Wrest Point Casino in Hobart have reported receiving messages featuring genuine reservation summaries, including actual booking numbers, room types, and correct check-in and check-out dates. The fraudulent messages claim that the credit card used for the booking has been blocked by the issuing bank and urge recipients to click a link to update and verify their payment details to prevent reservation cancellation.
RMS Chief Executive Adam Seskis issued an apology, noting that scams are becoming increasingly sophisticated. However, he confirmed that credit card and other payment details were not accessed during the initial hack.
Affected Properties and Providers
The RMS booking management system is utilized by more than 6,000 hotels, holiday parks, and serviced apartments globally. In Australia, affected providers include:
- Federal Group, which operates Wrest Point Casino and Country Club in Tasmania
- ALH Hotels, operators of Nightcap and Nightelier accommodation
- Discovery Parks, including its resort at Cradle Mountain
- Interstate holiday park operators such as BIG4, Reflections, and G'day Parks
Expert Advice and Verification
Experts and company officials have outlined practical steps for anyone who receives suspicious communications:
- Do not click links: Delete suspicious messages immediately and do not forward them.
- Secure devices: If a link was clicked, run antivirus software and change compromised passwords.
- Contact financial institutions: Anyone who inadvertently shared payment details should contact their bank immediately.
- Verify independently: Affected providers, including Wrest Point, have been emailing guests to detail how genuine contact is made. Travellers can verify alerts by contacting accommodation providers directly through official published phone numbers or websites.
University of Tasmania Adjunct Professor and cybersecurity expert Joel Scanlan stated that while third-party systems are common targets for hackers due to the aggregation of data, they often possess greater security resources than individual hotels could afford independently. He noted that such incidents highlight the importance of knowing what personal data is exposed and remaining vigilant against targeted phishing attempts.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Tradier Brokerage Data Breach Investigation Launched Following Vendor Cyberattack
 Navigate360 Data Breach Investigation Opened Following School Tip-Line Exposure
 Del Monte Foods Investigates Data Breach Following Ransomware Attack
 Law Firm Probes BCD Travel Data Breach Following Third-Party Cyber Attack
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 Madhya Pradesh Government Plans Revenue Generation from 117-Year-Old Edward Villa in Mumbai Through Leasing
 iPhone 18 Pro Named TechRadar Product of the Year 2026
 Google Project Suncatcher Runs Gemma 4 AI on Orbiting Satellite and Receives First Response
 Gender Disparities in Eye Care Access Across India Examined
 Satellite Images Show Cyclone Arnab Weakening Over India As New System Brews
 Expanding Green and Blue Spaces Crucial for India's Economic and Public Health, Reports Indicate