U.S. and European Police Seize Virtualine Bullet‑Proof Hosting Service Tied to Ransomware, Phishing and Child‑Abuse Content
· GlobeWire Daily Editorial Desk · Source: www.bleepingcomputer.com
Image: BleepingComputer · Photo source · Resized and letterboxed to 16:9; no AI generation
Overview
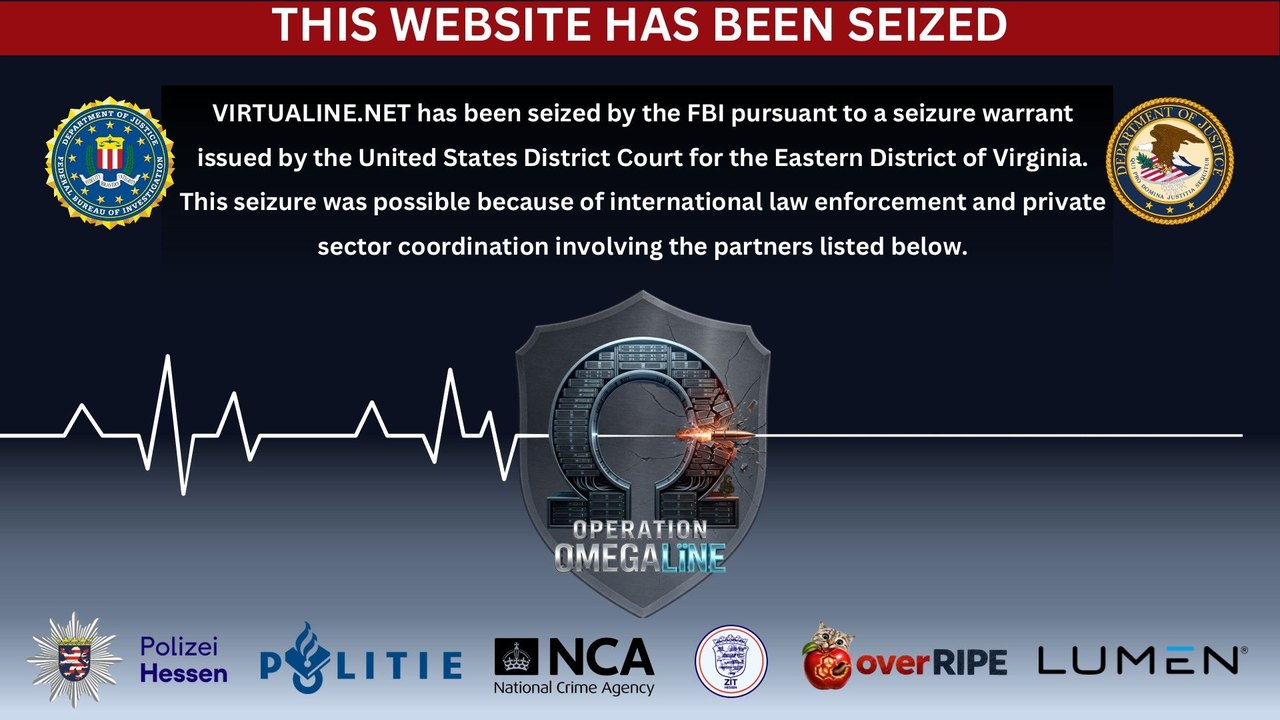
U.S. law‑enforcement agencies, together with partners in Germany, the Netherlands and the United Kingdom, have taken control of the primary domain virtualine.net. The service, marketed as a “bullet‑proof” hosting platform, was advertised on cyber‑crime forums under several aliases – Secury, Massgod, Spamhouse, Lanedo and Omegatech – and promised to shield customers from legal complaints and law‑enforcement requests.
Investigation and Seizure
- Agencies involved: U.S. Department of Justice (DOJ) and FBI, Germany’s Polizei Hessen, the Netherlands’ Politie Midden‑Nederland, the U.K.’s National Crime Agency, plus private partners OverRIPE and Lumen.
- Action taken: The FBI seized the domain *virtualine.net* and Dutch police confiscated dozens of physical servers in Limburg, taking hundreds of virtual servers offline.
- Data recovered: More than 3,000 Virtualine customer records were retrieved, and follow‑up investigations against those accounts are ongoing, according to Dutch authorities.
Alleged Illegal Activities
The DOJ confirmed that Virtualine marketed services for “illegal/black‑hat activities,” including:
- Phishing and spam campaigns
- Card‑ing (credit‑card fraud)
- Port scanning and other reconnaissance
- Hosting of ransomware and botnet infrastructure
- Distribution of child‑abuse material (CAI)
While the operator claimed to draw a line at child‑related content, investigators say Virtualine knowingly hosted a forum that promoted CAI, ignored repeated takedown notices from law‑enforcement, the National Center for Missing & Exploited Children (NCMEC) and a victim’s attorney, and later helped the forum migrate to a new site.
Financial Links and Money Laundering
- Bitcoin payments: Virtualine accepted direct Bitcoin payments through unhosted wallet addresses, allowing criminal customers to bypass exchange compliance checks (Chainalysis).
- Laundering: Chainalysis reported that the service “laundered” those proceeds to conceal their origin.
- Flow analysis (TRM report, 2024):
- Ransomware groups accounted for ~5 % of Virtualine’s incoming funds.
- A Russian‑language drug marketplace contributed ~44 %.
- Large sextortion schemes and a cryptocurrency mixer were also major sources.
- The StealC infostealer received regular payments throughout 2024.
Impact and Ongoing Risks
- Infrastructure: Researchers note that Virtualine’s network prefixes now show very low routing visibility, suggesting much of the hardware may be offline, but the service remains partially reachable.
- Customer exposure: The seized data includes thousands of accounts that may have been used for ongoing cyber‑crime campaigns. Victims should monitor for phishing, ransomware or credential‑theft attempts that reference these hosts.
- Verification: The seizure was announced in a DOJ press release and corroborated by Dutch police statements. Independent security firms (Silent Push, Chainalysis, TRM) have published supporting analyses.
Practical Takeaways for Defenders
- Check for Virtualine IPs: Update firewall and IDS/IPS blocklists with the known IPv4/IPv6 prefixes disclosed by researchers.
- Audit Bitcoin wallets: Organizations that received payments from addresses linked to Virtualine should consider transaction‑monitoring for possible money‑laundering exposure.
- Monitor threat‑intel feeds: Many ransomware groups now need new hosting providers; watch for fresh bullet‑proof services emerging after this takedown.
- Verify claims: Use official DOJ and Dutch police releases, plus the publicly available Silent Push blog post, to confirm the scope of the operation before acting on rumors.
How to Verify the Announcement
- Visit the U.S. DOJ newsroom (justice.gov) and search for “Virtualine” press release dated 2024‑09‑XX.
- Review the Dutch National Police (Politie) press release, also available on their website, for details on the server seizures.
- Consult the Chainalysis blog and TRM’s “Virtualine Financial Flow” report for the blockchain‑analysis findings.
- Cross‑reference with independent security blogs (e.g., Silent Push) that captured the operator’s open‑letter response on *virtualine.org*.
--- *The article is based solely on publicly released statements and third‑party analyses. No original reporting was conducted.*
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 FBI and International Partners Seize Infrastructure of Bulletproof Hosting Service Virtualine
 Content creator faces backlash after hosting public divorce ceremony
 Investigation Highlights Ongoing Scale of Child-on-Child Sexual Abuse in English and Welsh Schools
 New York Knicks Face Criticism Over Phishing Test Disguised as Championship Ring Offer
Related coverage
Related reporting available at publication.
FBI and International Partners Seize Infrastructure of Bulletproof Hosting Service VirtualineContent creator faces backlash after hosting public divorce ceremonyInvestigation Highlights Ongoing Scale of Child-on-Child Sexual Abuse in English and Welsh SchoolsNew York Knicks Face Criticism Over Phishing Test Disguised as Championship Ring Offer Proposed Class Action Settlement Offered Over The Merchant of Tennis Data Incident
 PHP2Shell Exploit Attempts Hit Millions Amid Mirai Malware Deployment Efforts