PHP2Shell Exploit Attempts Hit Millions Amid Mirai Malware Deployment Efforts
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
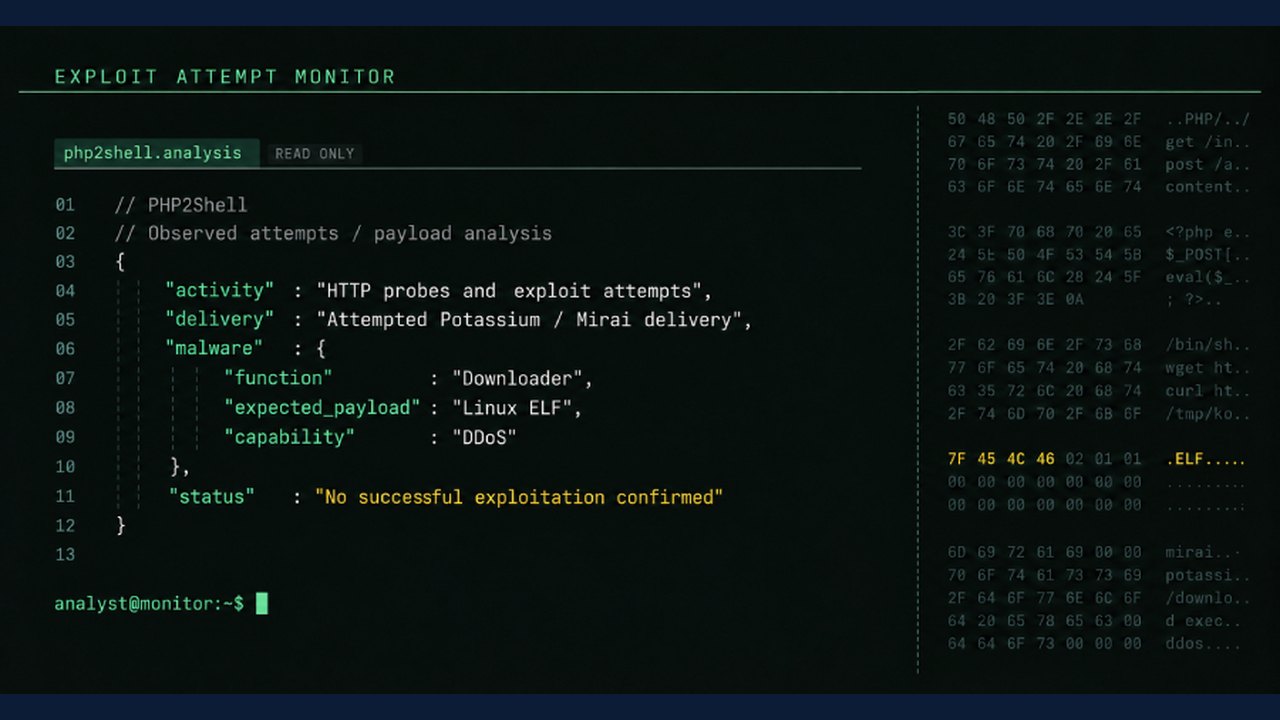
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Security researchers and telemetry providers have observed millions of automated scanning and exploit attempts targeting recently disclosed PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619). While malicious actors have rapidly weaponized the flaws to attempt deployments of a Mirai botnet variant known as Potassium, threat intelligence firms note that achieving reliable remote code execution (RCE) remains difficult due to protections such as Address Space Layout Randomization (ASLR).
Overview of the PHP2Shell Flaws
- Affected Components: Unauthenticated remote code execution flaws in the PHP engine, impacting versions prior to the patched releases.
- Patched Versions: Fixed in PHP versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35.
- Origin: The underlying vulnerable code dates back to PHP 5.4, meaning applications running on unsupported PHP branches without engine updates remain exposed regardless of clean application-level code.
Attack Activity and Botnet Campaigns
- Volume: Cloudflare reported that scanning and exploitation attempts surged from tens of thousands shortly after public disclosure to millions by October 22, 2026.
- Payloads: Observed campaigns attempt to rope infected systems into the Potassium botnet variant, utilizing downloader capabilities, C2 infrastructure, and DDoS functionalities.
- Tooling: Security firms like SOCRadar identified exposed attacker servers hosting Python exploit tooling (such as `aslr_exploit.py`) and screening scripts designed to check live websites for prerequisites.
Practical Implications and Verification
- Precautionary Outages: Out of an abundance of caution, various government, educational, and healthcare websites across Asia, Europe, and North America initiated temporary shutdowns while applying updates.
- Mitigation: Organizations running supported versions are advised to apply official patches immediately. Those on unsupported branches (such as PHP 7.4, 8.0, or 8.1) should migrate to a supported branch or utilize distribution backports.
- Verification: Organizations can verify exposure by checking their PHP engine versions against official vendor bulletins and reviewing server access logs for anomalous unauthenticated HTTP requests targeting session handlers.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Hackers Exploit Cisco SD-WAN Vulnerability to Deploy Custom KeyDrift Malware
 Hackers Hijack OVHcloud CLI Releases to Distribute Secret-Stealing Malware
 Sophisticated Malware Campaign Targets Online Poker Players
 Binance Investigates Major Security Incident as Millions Frozen On-Chain
Related coverage
Related reporting available at publication.
Hackers Exploit Cisco SD-WAN Vulnerability to Deploy Custom KeyDrift MalwareHackers Hijack OVHcloud CLI Releases to Distribute Secret-Stealing MalwareSophisticated Malware Campaign Targets Online Poker PlayersBinance Investigates Major Security Incident as Millions Frozen On-Chain NSE Scrutinizes Network Vulnerabilities Amid Escalating AI-Driven Cyber Threats
 NSE Highlights Broker Lapses in Margin Trading, Client Funds, and Cybersecurity