China-Linked Hackers Exploited VMware ESX Zero-Day to Reduce Audit Trail Visibility
· GlobeWire Daily Tech Desk · Source: thehackernews.com
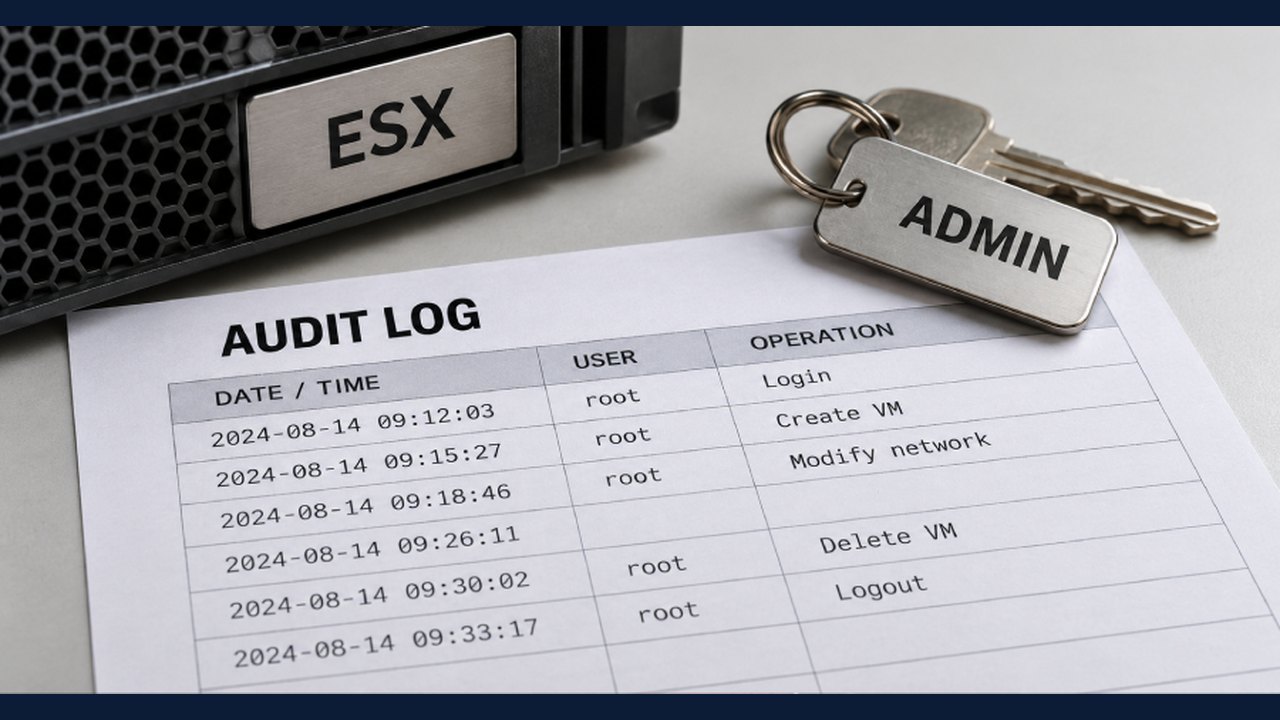
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Federal authorities have added a security flaw affecting Broadcom VMware ESX to the Known Exploited Vulnerabilities catalog following reports that a China-linked threat group weaponized it against the U.S. legal sector. Cybersecurity reports indicate the flaw was exploited as a zero-day to diminish audit trail visibility.
Vulnerability Overview and Attribution
The vulnerability, identified as CVE-2026-41709 with a CVSS score of 2.7, involves insufficient logging that allows an administrator-level malicious actor to execute certain operations without generating standard logs. Cybersecurity firm CrowdStrike reported that the threat actor Warp Panda, also known by alternative names such as Armory Castle, Clay Typhoon, and VerdantBamboo, utilized the flaw in early 2026.
- Affected Software: Broadcom VMware ESX
- Identified Flaw: CVE-2026-41709
- Reported Impact: Reduced audit trail visibility during unauthorized operations
Attack Methods and TACTICS
According to published threat intelligence reports, Warp Panda targets internet-facing edge devices using zero-day vulnerabilities and custom malware to establish covert and persistent access. The group has historically focused on edge infrastructure, including Citrix NetScaler and Ivanti Connect Secure appliances, alongside other recent campaigns targeting remote support software.
- Initial access gained via internet-facing edge devices
- Lateral movement into VMware vCenter environments
- Deployment of custom persistence tools such as BRICKSTORM and SharpStorm
- Cloud service targeting for session token extraction and unauthorized multi-factor authentication device registration
Practical Implications and Verification
Organizations operating affected VMware environments should review official vendor advisories and apply recommended updates. Federal Civilian Executive Branch agencies have been advised by the U.S. Cybersecurity and Infrastructure Security Agency to implement patches by November 11, 2026. Administrators can verify applicable patches and remediation guidance directly through Broadcom's security advisory portal and review catalog entries on the official CISA website.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Apple Backports CoreGraphics Zero-Day Patches to Older iPhones and iPads
 CAG Impact Report Highlights ₹4,251 Crore in Audit-Linked Recoveries for FY26
 Chinese Hackers Chain PHP2Shell to Root Servers and Breach US Government-Affiliated Firewalls
 Drupal Issues Urgent Patch for Critical Commerce Core Flaw Actively Exploited in Attacks
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 Madhya Pradesh Government Plans Revenue Generation from 117-Year-Old Edward Villa in Mumbai Through Leasing
 iPhone 18 Pro Named TechRadar Product of the Year 2026
 Google Project Suncatcher Runs Gemma 4 AI on Orbiting Satellite and Receives First Response
 Gender Disparities in Eye Care Access Across India Examined
 Satellite Images Show Cyclone Arnab Weakening Over India As New System Brews
 Expanding Green and Blue Spaces Crucial for India's Economic and Public Health, Reports Indicate