Go Issues Emergency Update Blocking Eight CA Keys Over Undisclosed Security Concerns
· GlobeWire Daily Tech Desk · Source: thehackernews.com
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
The Go programming language team released Go 1.27.3 and Go 1.26.10 on October 20, incorporating an urgent update that rejects certificate chains passing through eight specific intermediate certificate authority keys. Programs built using these new releases will refuse connections to servers whose certificates were issued under the blocked keys.
Update Details and Scope
- Releases: Go 1.27.3 and Go 1.26.10.
- Action: Rejects certificate chains passing through eight intermediate CA keys.
- Implementation: The filter hashes each certificate's public key, catching cross-signed copies as well.
- Scope: Applies in Go's native verifier and macOS/Windows OS verification paths without a disable switch.
Background and Connections
While the Go team stated the action stems from unspecified security concerns regarding the operation of an unnamed certificate authority, public commenters matched the blocked SHA-256 hashes to eMudhra intermediate keys. These include six TLS intermediates under emSign Root TLS CA - G3—matching entries added to Mozilla's OneCRL list on October 17—and two code-signing intermediates.
Action status across other vendors like Chrome, Apple, or Microsoft remains unestablished. As of October 20, eMudhra had published no notice regarding the intermediates in its repository, and official statements from Mozilla and Go have not detailed the exact catalysts for the security actions.
Practical Implications and Verification
Because Go's verifier lacks built-in revocation checking, blocking keys requires shipping them directly within a software release. Developers must rebuild their applications using supported Go versions to enforce the filter. Programs relying on private deployments that intentionally trust any of the eight keys will also experience connection failures.
To verify official announcements and updates, administrators should consult the official Go download page and security advisory channels.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
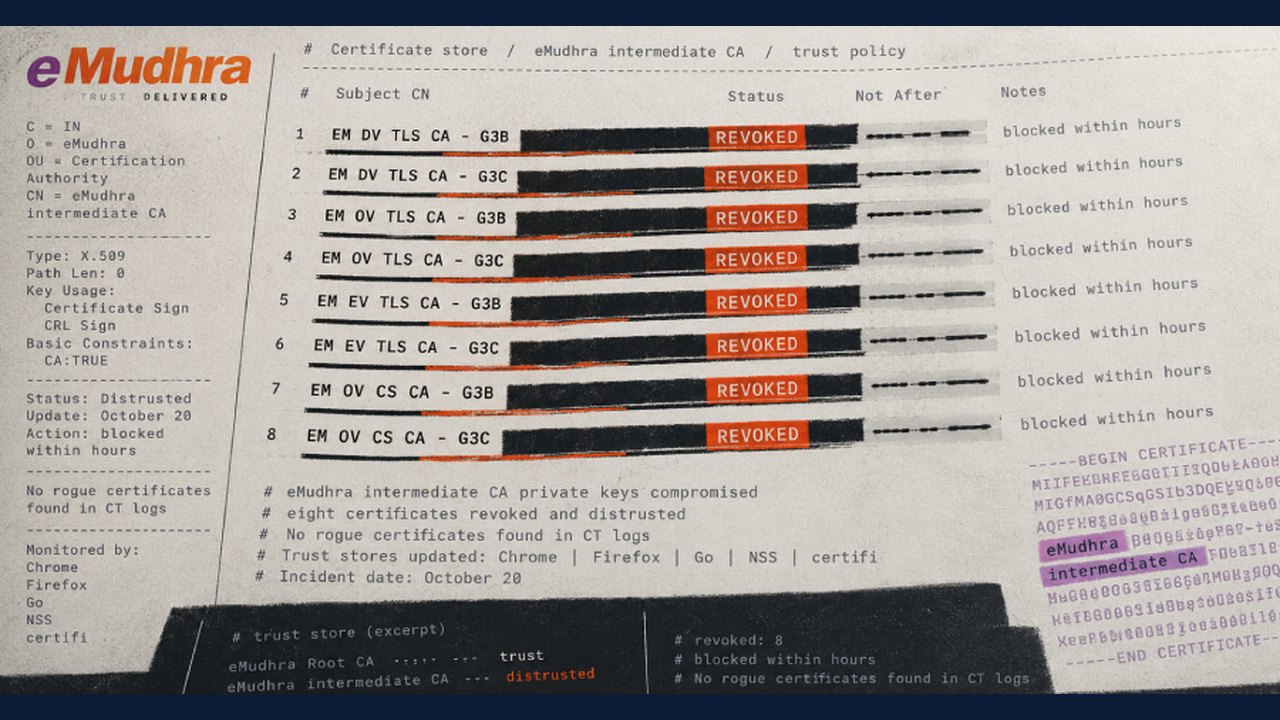 Eight eMudhra CA Keys Compromised, Triggering Emergency Fixes Across Browsers and Software
 TeamViewer Issues Security Patch for Critical Vulnerability (CVE-2026-111585)
 PHP Issues Emergency Patches for Critical 'PHP2Shell' RCE Flaws
 Stubble Burning Causes Visibility Issues and Health Concerns in Kushinagar, Uttar Pradesh