Fake AI Apps Abuse Signed Executables to Deploy Cryptominers
· GlobeWire Daily Editorial Desk · Source: thehackernews.com
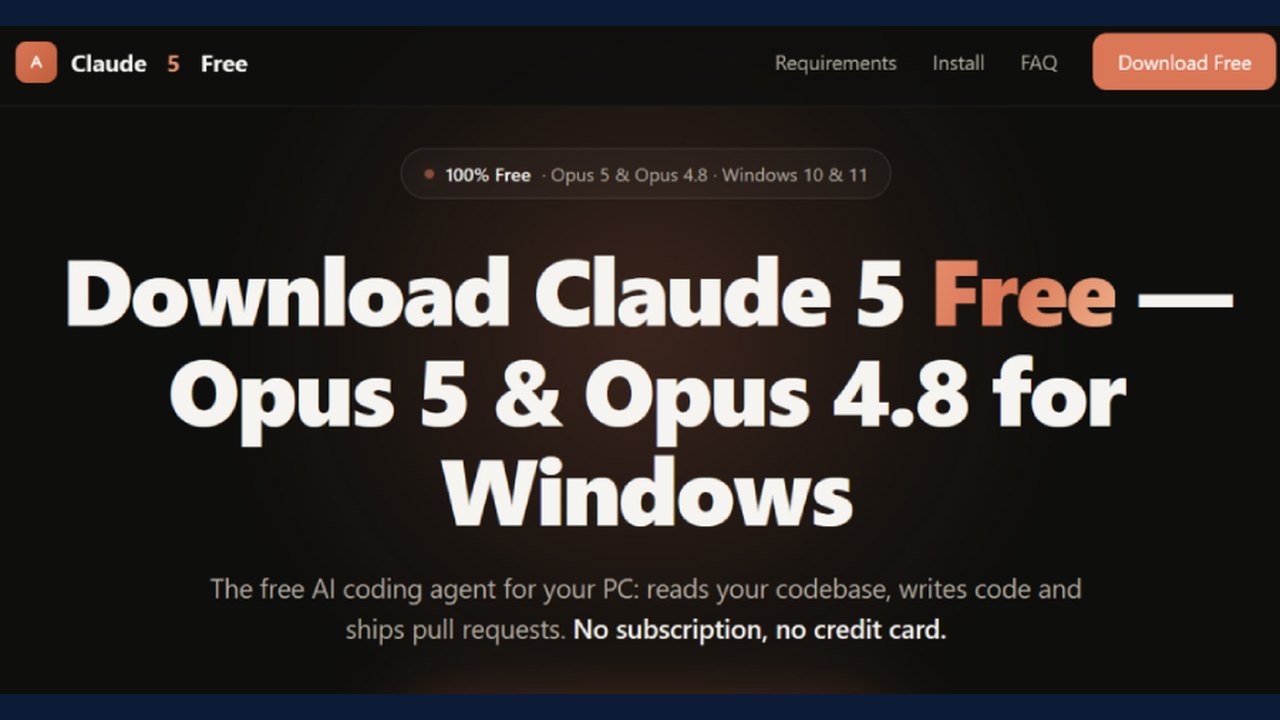
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Security researchers have uncovered a malicious campaign dubbed "Yoba" that distributes fake desktop applications for popular AI tools like Anthropic Claude and OpenAI ChatGPT. According to an analysis by Check Point Research, threat actors are leveraging fraudulent GitHub projects and SEO poisoning tactics to trick users into downloading malicious loaders and cryptocurrency miners.
How the Attack Works
The campaign involves setting up deceptive GitHub repositories and dedicated GitHub.io landing pages advertising non-existent or futuristic AI desktop apps, such as GPT-5.6 Sol, GPT-6 Astra, and Claude Opus. To make the downloads appear legitimate, the attackers utilize a technique known as DLL sideloading.
- Legitimate Binaries: The downloaded ZIP archives contain authentic, signed executables from OpenAI or Anthropic (such as Setup.exe).
- Malicious Sideloading: A malicious DLL file named `winmm.dll` is placed alongside the legitimate executable, allowing the malware to execute indirectly and bypass standard security protections.
Evasion and Anti-Analysis Techniques
Reported findings indicate that the YobaDropper incorporates several sophisticated checks designed to evade sandbox environments and security analysis:
- Checksum Verification: The malicious DLL verifies the host executable's name via a hard-coded hash value, ensuring it only runs when launched as intended.
- Delay Execution: The malware utilizes extensive sleep loops totaling over 12 days to stall execution and bypass automated sandbox timeouts.
- Geographic Exclusion: Infections actively skip machines configured with specific regional keyboard layouts, including Russia, Belarus, and several Central Asian nations.
Command-and-Control and Final Payload
Once initial checks pass, the infection chain initiates a second DLL sideloading process using system utilities like `wmpdmc.exe`. The loader establishes persistence through a scheduled task and utilizes a Domain Generation Algorithm (DGA) along with Google's DNS-over-HTTPS (DoH) API to fetch encrypted commands from Telegram and file-hosting services. Ultimately, the final payload injects an XMRig cryptocurrency miner into legitimate system processes like `svchost.exe`.
Practical Implications and Verification
This activity highlights how threat actors exploit public interest in artificial intelligence tools and abuse trusted platforms like GitHub. Users are advised to exercise caution when downloading desktop clients for AI services, ensuring software is obtained strictly from official vendor websites. Original announcements and technical indicators can be verified through security research publications from firms like Check Point Research.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 New Cybercrime Campaign Spreads Cryptojacking Malware via Fake AI Apps and SEO Poisoning
 Google Launches Connected Apps Platform to Expand AI Agent Integration
 Shipwords Framework Launches to Deploy AI Media Sites per Keyword on Cloudflare
 Exploring Third-Party AI Apps for Ring Security: Features, Costs, and Privacy Risks
Related coverage
Related reporting available at publication.
New Cybercrime Campaign Spreads Cryptojacking Malware via Fake AI Apps and SEO PoisoningGoogle Launches Connected Apps Platform to Expand AI Agent IntegrationShipwords Framework Launches to Deploy AI Media Sites per Keyword on CloudflareExploring Third-Party AI Apps for Ring Security: Features, Costs, and Privacy Risks FADU Proposes Moving File Systems Inside SSDs to Bypass AI Storage CPUs
 Experts and Advocates File Briefs Supporting Fair Use in AI Training