GitHub Repository Details Sandbox Extension TOCTOU Bug Involving Symlinks
· GlobeWire Daily Editorial Desk · Source: github.com
Image: GitHub · Photo source · Resized and letterboxed to 16:9; no AI generation
A recently highlighted issue on GitHub, published by user speedyfriend433 under the repository name sandbox_extension-TOCTOU-bug, details a Time-of-Check to Time-of-Use (TOCTOU) vulnerability involving sandbox extensions and symbolic links. According to the technical description provided in the repository, the mechanism known as sandbox_extension_issue_file resolves symlinks when an issue is raised, but it reportedly fails to enforce the `SANDBOX_EXTENSION_NOFOLLOW` flag.
Technical Mechanism of the Reported Behavior
- Symlink Resolution: The reported behavior indicates that an application can issue an extension for a symbolic link that points to a sandboxed file.
- Target Swapping: The symlink can then be swapped to point to a target located outside of the designated sandbox.
- Extension Consumption: Finally, the extension is consumed, which the author states allows reading the target file.
- Deterministic Execution: The repository notes that the kernel does not verify whether the access path matches the extension token path, making the process deterministic without requiring race timing.
Practical Implications and Context
According to the repository documentation, this behavior is described in the context of system file access limitations. However, the author asserts that the platform provider—specifically referenced as Apple—does not currently view this specific behavior as a security issue.
How to Verify and Check
- Review the Source: Independent security researchers and developers can review the technical details directly in the public GitHub repository at `speedyfriend433/sandbox_extension-TOCTOU-bug`.
- Assess Environment Risk: Organizations and developers working with sandbox extensions can audit their own implementations to understand how symlinks are handled in their specific environments.
- Monitor Vendor Guidance: Users should consult official security advisories and documentation from the platform vendor for any updates regarding sandbox extension behavior and policy.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 GitHub Introduces Security Extension for the Copilot App in Public Preview
 New GitHub Repository Focuses on Model-Specific Camera Hardware Research and Local Software
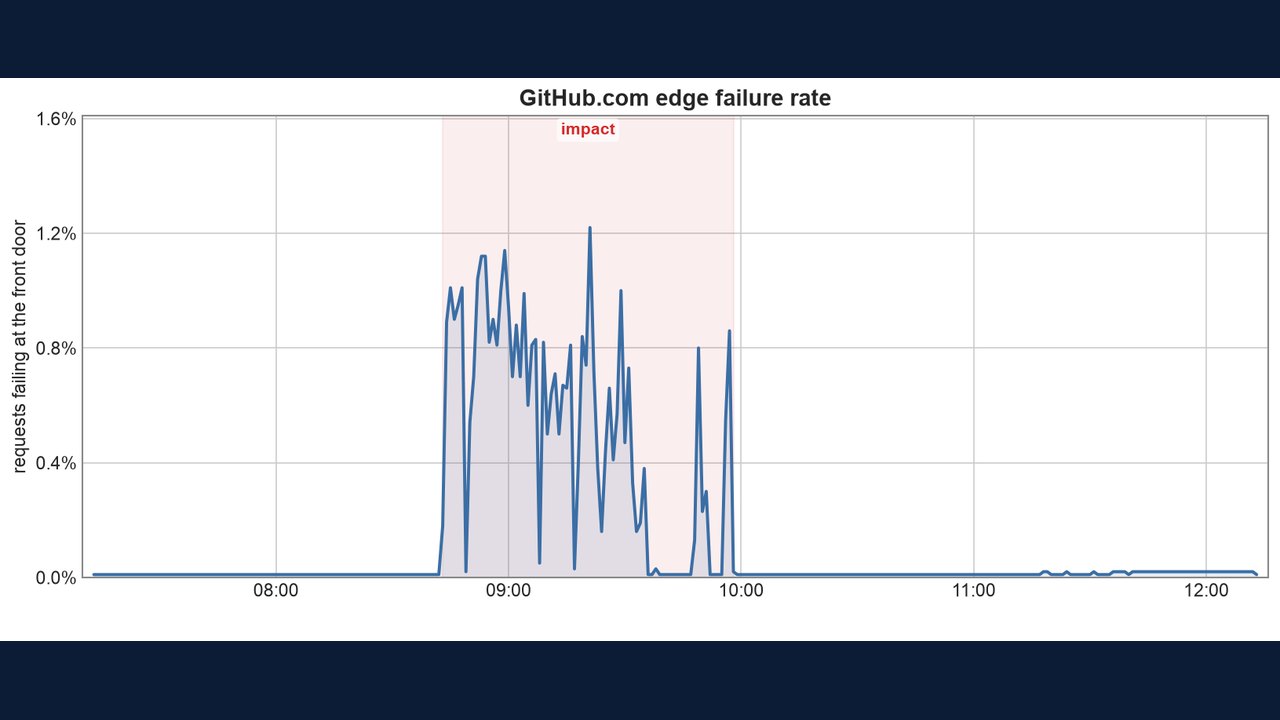 GitHub Details Infrastructure Progress, Regional Migrations, and Recent Outages in Availability Report
 GitHub Addresses Incident Involving Incorrectly Deleted Enterprise Managed User Accounts
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 Madhya Pradesh Government Plans Revenue Generation from 117-Year-Old Edward Villa in Mumbai Through Leasing
 iPhone 18 Pro Named TechRadar Product of the Year 2026
 Google Project Suncatcher Runs Gemma 4 AI on Orbiting Satellite and Receives First Response
 Gender Disparities in Eye Care Access Across India Examined
 Satellite Images Show Cyclone Arnab Weakening Over India As New System Brews
 Expanding Green and Blue Spaces Crucial for India's Economic and Public Health, Reports Indicate