Security Researchers Warn of Bluetooth Flaws in Warehouse Barcode Scanners
· GlobeWire Daily Editorial Desk · Source: www.techradar.com
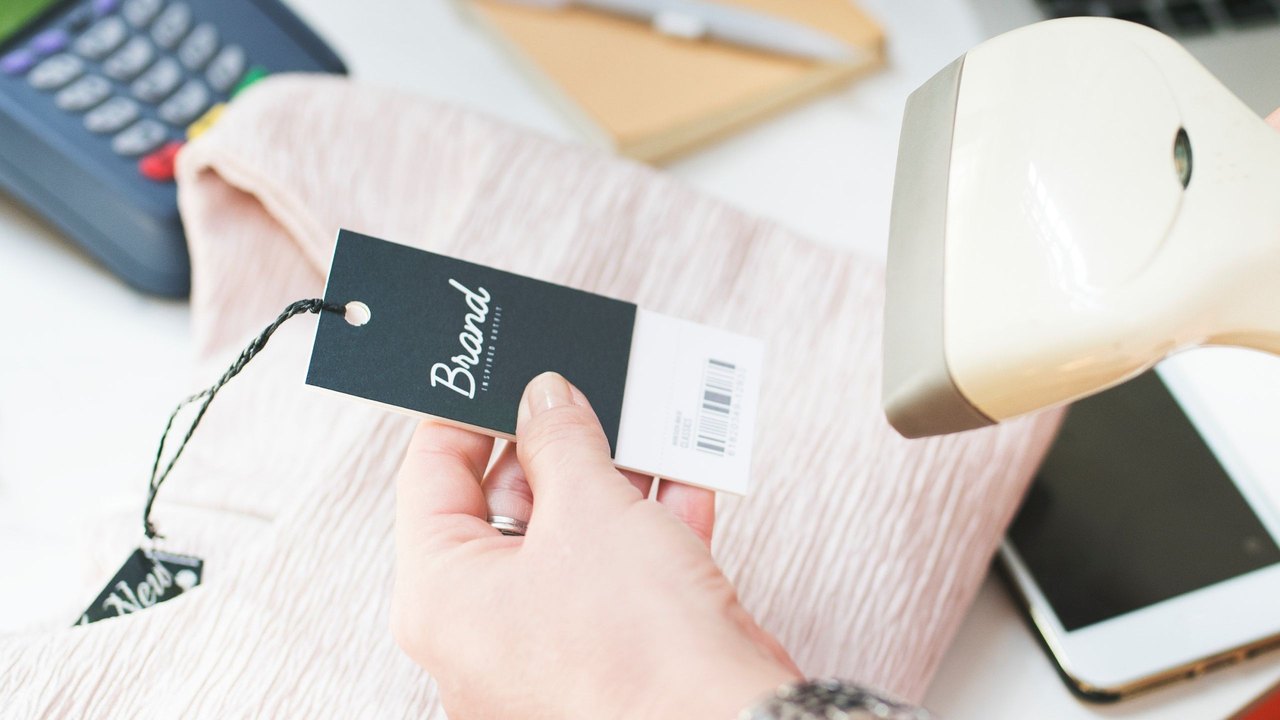
Image: TechRadar · Photo source · Resized and letterboxed to 16:9; no AI generation
Potential Vulnerabilities in Warehouse Hardware
Security researchers have reported that certain warehouse barcode scanners may contain Bluetooth-related security flaws that could potentially allow unauthorized access to connected enterprise networks. According to findings shared by cybersecurity firm Kaspersky, the vulnerability stems from a lack of authentication between handheld scanners and their base stations.
Researchers claim that an attacker could theoretically spoof scanner input, inject malicious keystrokes, and pivot further into a company's IT infrastructure. The scanner itself serves merely as an entry point rather than the final objective, with broader risks including potential data theft or ransomware deployment.
Key Findings and Scope
- Lack of Authentication: Communication between the handheld scanner and base station reportedly lacks robust verification methods.
- Keystroke Injection: Attackers could potentially simulate legitimate user inputs to interact with connected workstations.
- Industry Impact: While specific manufacturer names and vulnerable device counts remain undisclosed, the hardware is reportedly widely used across warehousing, retail, and logistics.
Kaspersky noted that similar scenarios could theoretically apply to other connected operational devices, such as portable data terminals and thermal printers, potentially exposing Warehouse Management Systems (WMS).
Recommended Mitigation Steps
To address these reported risks, security experts advise organizations to implement several defensive measures:
- Enforce strict device authentication and verify all new hardware before network connection.
- Disable unused Bluetooth interfaces on operational devices.
- Segment warehouse networks to limit lateral movement.
- Apply security updates promptly to both endpoint devices and management systems.
- Restrict account permissions to the minimum necessary requirements.
How to Verify and Investigate
Organizations utilizing wireless barcode scanners and similar peripherals should consult directly with their hardware vendors to confirm whether their devices rely on secure authentication mechanisms. Reviewing network monitoring logs for anomalous peripheral behavior and conducting internal security assessments can also help identify unauthorized access attempts.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Ransomware Affiliates Deploy AI Agents in 'Phantom' Framework to Automate Intrusions, Researchers Find
 CISA Adds Ivanti Connect Secure Flaws to KEV Catalog Following Active Exploit Chain
 Pakistani Court Sentences Human‑Rights Lawyers to 10 Years Over Alleged Security Breach During England’s 2024 Test Tour
 Pakistani Human Rights Lawyers Sentenced in Security Convoy Case
Related coverage
Related reporting available at publication.
Ransomware Affiliates Deploy AI Agents in 'Phantom' Framework to Automate Intrusions, Researchers FindCISA Adds Ivanti Connect Secure Flaws to KEV Catalog Following Active Exploit ChainPakistani Court Sentences Human‑Rights Lawyers to 10 Years Over Alleged Security Breach During England’s 2024 Test TourPakistani Human Rights Lawyers Sentenced in Security Convoy Case New Cybercrime Campaign Spreads Cryptojacking Malware via Fake AI Apps and SEO Poisoning
 Hackers Target High-Stakes Online Poker Players with Screen-Viewing Malware