Attackers Hijacked Over 300 Tor Exit Relays to Intercept SSH Connections
· GlobeWire Daily Tech Desk · Source: thehackernews.com
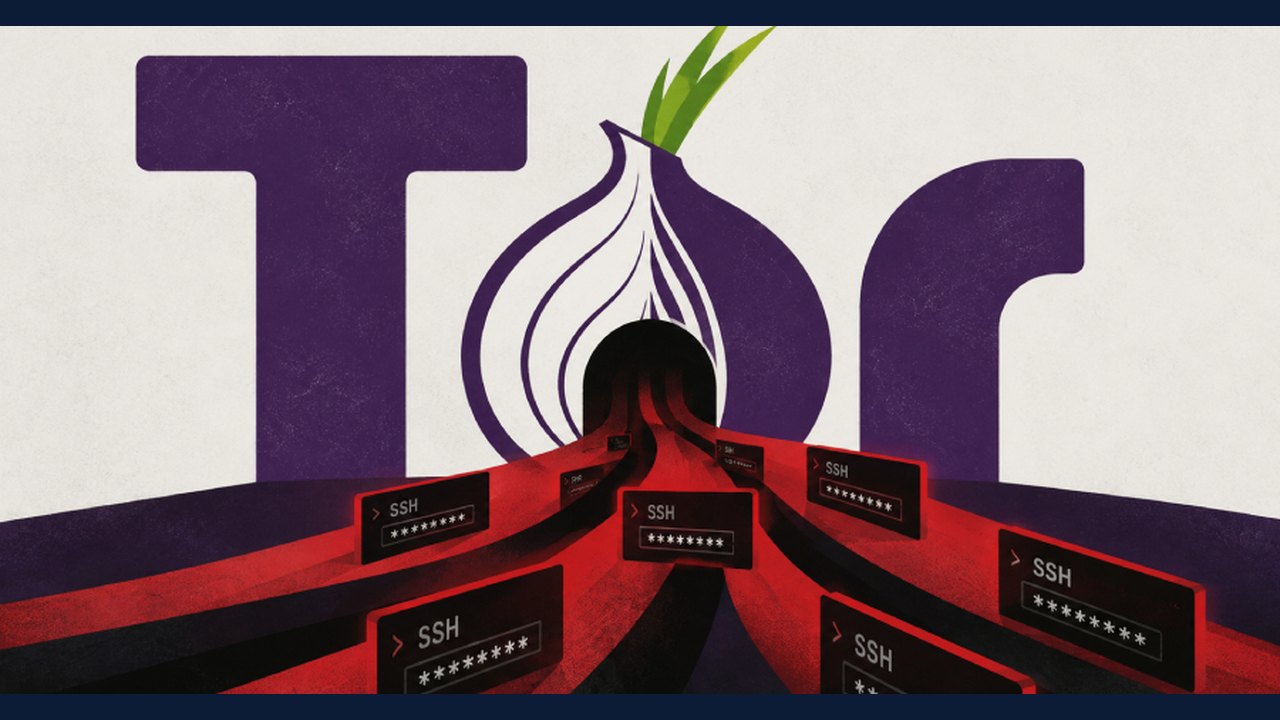
Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
Security researchers and the Tor Project reported that attackers compromised over 300 Tor exit relays in early October to redirect SSH traffic to malicious interception servers designed to capture login credentials. The incident affected Tor's network capacity temporarily before directory authorities removed the malicious relays from consensus.
Overview of the Tor Relay Incident
- Timeline: The activity occurred between October 1 and October 5.
- Scale: A security researcher known as kaba identified 333 relays redirecting SSH, while directory analyses noted up to 377 affected relays.
- Impact: At its peak on October 4, the modified relays accounted for 7.46% of Tor's exit capacity.
How the Interception Worked
Attackers gained administrative access to underlying Linux hosts and modified `torrc` configuration files. By altering exit policies, they enabled port 22 (SSH) on relays that previously blocked it, while simultaneously disrupting encrypted mail ports.
- Traffic Redirection: SSH connections through affected exits were routed to one of 12 interception servers.
- Host Key Warnings: Users connecting via password authentication encountered altered or unfamiliar host keys. Accepting these keys allowed attackers to record passwords.
- Key-Based Logins Unaffected: SSH connections utilizing cryptographic keys remained secure because session-unique signatures cannot be replayed against real servers.
Response and Remediation
The Tor Project's network health team detected the policy changes and coordinated with directory authorities to add `BadExit` and `MiddleOnly` flags. By October 5, all non-compliant relays were removed from the consensus list.
A prominent relay operator, Zimmer, reported that two of his servers were compromised via the Ebury OpenSSH backdoor, which survived routine reboots. Security experts recommend verifying relay configurations, checking for unauthorized `torrc` modifications, inspecting system files for the Ebury implant, and rotating all credentials if exposure is suspected.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
 Building Boom Puts 300,000 People in Path of Potential Himalayan Disasters, Study Warns
 Honda Reveals 1,300-HP Hybrid Passport Baja Spec to Conquer Trophy Truck Class
 Prime Video Unveils Scheduled November Lineup Featuring Major Originals and Gaming Connections
 Actor Asif Khan Reportedly Set to Exit Bigg Boss 20 After Lowest Audience Votes
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 Madhya Pradesh Government Plans Revenue Generation from 117-Year-Old Edward Villa in Mumbai Through Leasing
 iPhone 18 Pro Named TechRadar Product of the Year 2026
 Google Project Suncatcher Runs Gemma 4 AI on Orbiting Satellite and Receives First Response
 Gender Disparities in Eye Care Access Across India Examined
 Satellite Images Show Cyclone Arnab Weakening Over India As New System Brews
 Expanding Green and Blue Spaces Crucial for India's Economic and Public Health, Reports Indicate