CERT-UA Warns of Dahua IP Camera Hijacking via P2P Access and Auth Weaknesses
· GlobeWire Daily Tech Desk · Source: thehackernews.com

Image: The Hacker News · Photo source · Resized and letterboxed to 16:9; no AI generation
The Computer Emergency Response Team of Ukraine (CERT-UA) issued an alert warning about unauthorized remote access to Dahua video surveillance systems. According to reported information, attackers have compromised IP cameras and digital video recorders (DVRs), gaining access to video streams, altering device configurations, and creating unauthorized third-party accounts.
CERT-UA noted that the primary initial access vector involves the Easy4IP peer-to-peer (P2P) platform. The agency reported that device serial numbers feature a predictable structure containing a 10-character model prefix and a 5-character hexadecimal counter. This structure can allow attackers to perform brute-force attacks at scale to identify cloud-connected devices without triggering rate limits.
Key Findings and Attack Mechanisms
- P2P Platform Exploitation: Attackers leverage the Easy4IP platform to reach devices behind network address translation (NAT).
- Authentication Weaknesses: Intruders bypass authentication barriers using weak passwords or by exploiting known firmware vulnerabilities, specifically CVE-2021-33044 and CVE-2021-33045.
- Indicators of Compromise: CERT-UA highlighted audit logs showing authentication events using the native DVRIP protocol from a local address (127.0.0.1) as a sign of P2P access.
- Persistent Backdoors: Similar independent research by Hunt.io identified instances where threat actors installed persistent backdoor accounts ('p2pwn / p2password') that can survive password changes and factory resets on certain firmware.
Practical Implications and Recommendations
Security authorities advise organizations and individuals utilizing Dahua surveillance equipment to evaluate their exposure and implement defensive measures:
- Disable the P2P feature if remote monitoring is not strictly required.
- Avoid exposing surveillance devices directly to the public internet.
- Apply available firmware updates to mitigate known authentication bypass flaws.
To verify official advisories and technical indicators, consult the official CERT-UA or State Special Communications Service of Ukraine (SSSCIP) web portals for direct alerts.
AI-assisted reporting; source claims are attributed and have not been independently verified.
More to read
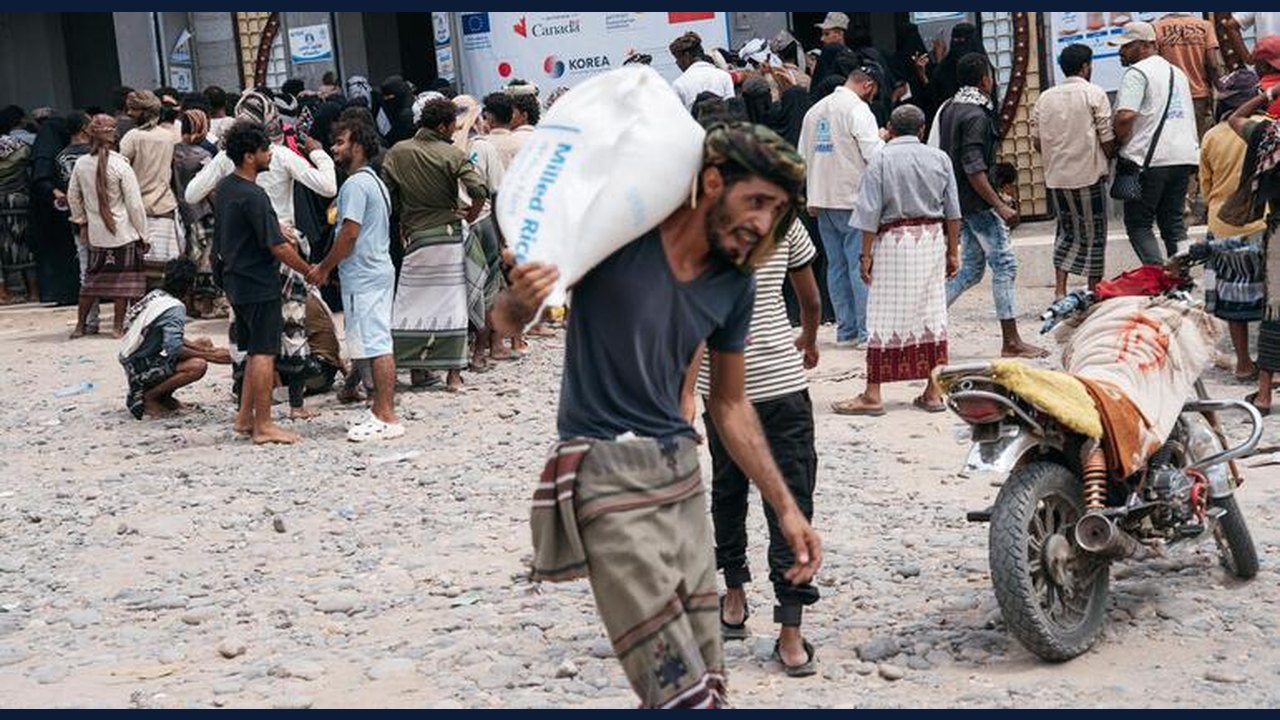 UNHCR Warns of Worsening Humanitarian Crisis and Access Dangers for Displaced People in Yemen
 Chrome Extensions With 13.4 Million Installs Caught Hijacking Searches
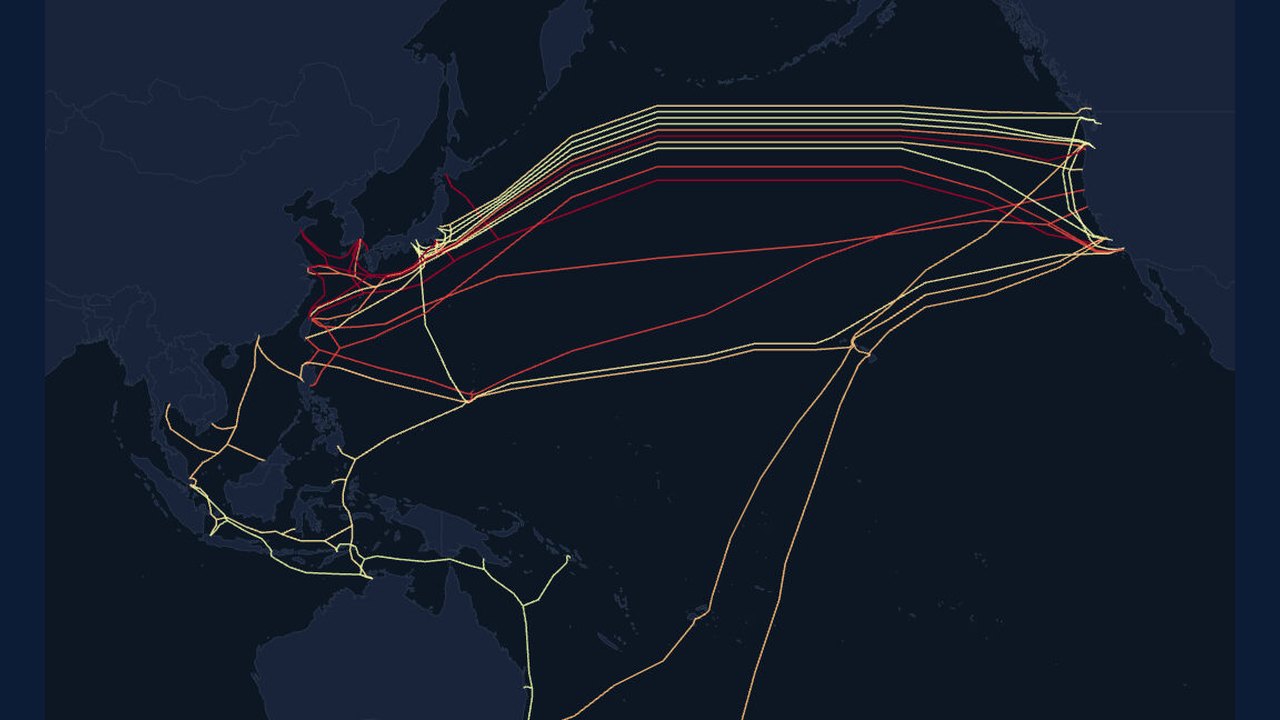 US tech subsea cables face heightened Pacific sabotage risks, report warns
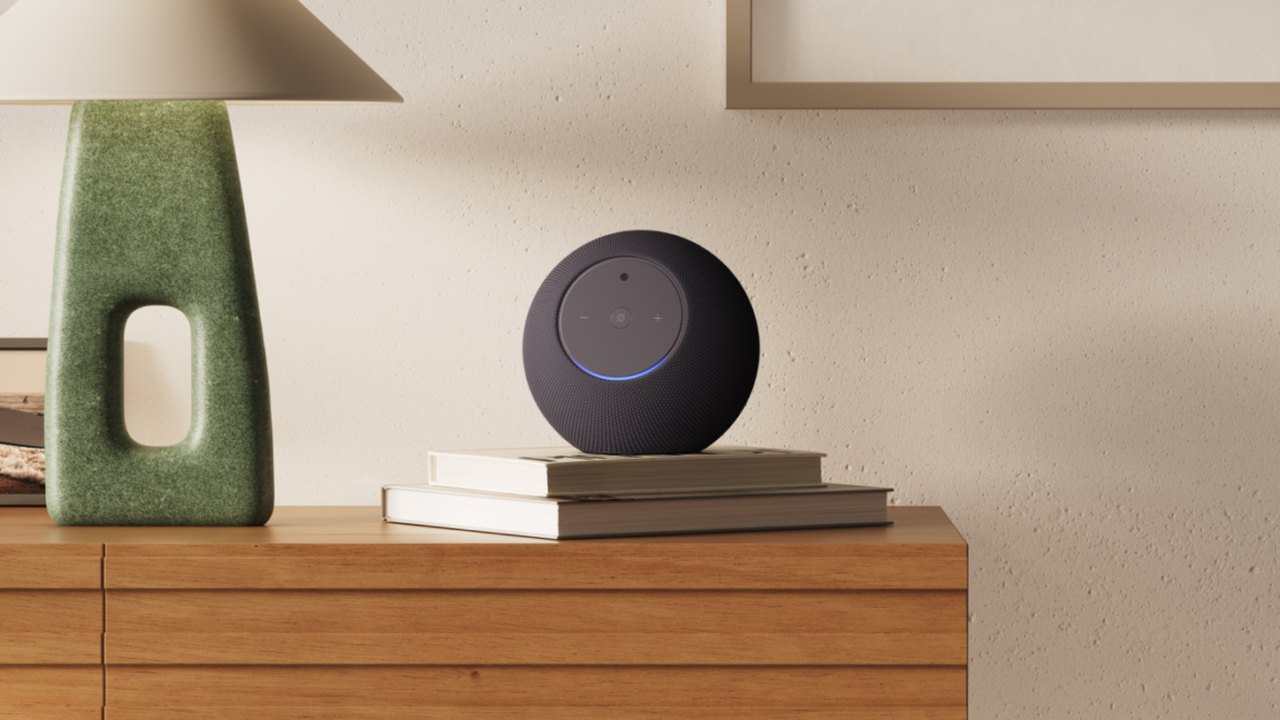 Amazon Adds Integrated Camera to Echo Studio Smart Speaker
Trending on GlobeWire Daily
Selected from recent coverage and related topics; not live search rankings.
 Madhya Pradesh Government Plans Revenue Generation from 117-Year-Old Edward Villa in Mumbai Through Leasing
 iPhone 18 Pro Named TechRadar Product of the Year 2026
 Google Project Suncatcher Runs Gemma 4 AI on Orbiting Satellite and Receives First Response
 Gender Disparities in Eye Care Access Across India Examined
 Satellite Images Show Cyclone Arnab Weakening Over India As New System Brews
 Expanding Green and Blue Spaces Crucial for India's Economic and Public Health, Reports Indicate